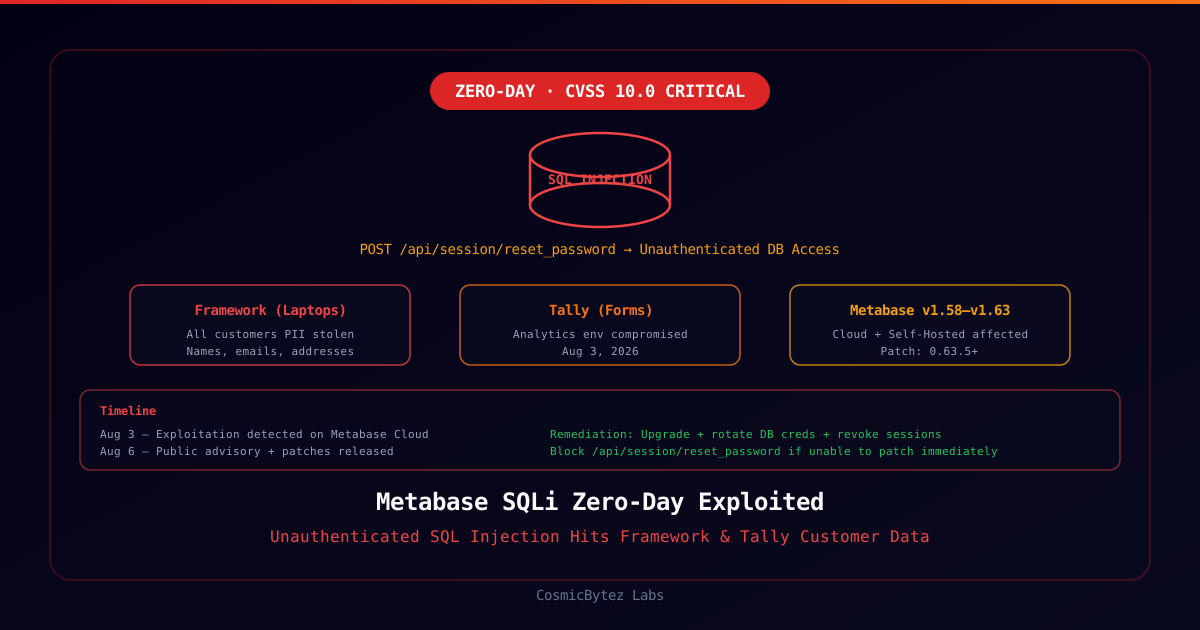
An unauthenticated SQL injection zero-day with a CVSS score of 10.0 in Metabase, one of the most widely deployed open-source business intelligence platforms, was actively exploited beginning August 3, 2026, resulting in confirmed customer data theft at laptop manufacturer Framework and online form builder Tally.
Metabase published patches on August 6, 2026. Organizations running affected versions — v1.58 through v1.63 — must update immediately.
What Happened
Metabase detected anomalous activity on its own cloud infrastructure on August 3, 2026, consistent with exploitation of a previously unknown vulnerability. Forensic investigation revealed a critical, unauthenticated SQL injection flaw in the password reset endpoint (/api/session/reset_password). Chained with a secondary API call to /api/user/current, the exploit allows an unauthenticated attacker to:
- Execute arbitrary SQL against all databases connected to the Metabase instance
- Extract admin credentials and configuration data
- Gain full administrative access to the Metabase installation
- Exfiltrate data from every database the Metabase service account can reach
Known Victims
Framework (laptop manufacturer) confirmed that attackers accessed customer records via its Metabase deployment. The stolen data included customer names, email addresses, phone numbers, and billing/shipping addresses. Payment card information was not stored in the affected system. Framework notified all affected customers and disclosed the breach publicly within six hours of learning of the attack — a transparency timeline that drew praise from the security community.
Tally (online form builder) confirmed its Metabase analytics environment was compromised on the same date, August 3.
Metabase has contacted law enforcement and retained an external forensic investigation firm.
Technical Details
Vulnerability
| Attribute | Value |
|---|---|
| Type | Unauthenticated SQL Injection |
| CVSS Score | 10.0 (Critical) |
| Attack Vector | Network |
| Authentication | None required |
| Privileges Required | None |
| User Interaction | None |
| Entry Point | POST /api/session/reset_password |
| CVE | None assigned as of August 7, 2026 |
| GitHub Advisory | GHSA-vwf4-m7j8-wcjf |
Attack Path
1. Attacker identifies internet-accessible Metabase instance (cloud or self-hosted)
2. Sends crafted POST request to /api/session/reset_password (no auth required)
3. SQL injection payload executes against Metabase's underlying database
4. Follow-up GET to /api/user/current extracts admin session data
5. Attacker gains full Metabase admin access
6. All connected databases exposed — credentials stolen, data exfiltrated
The vulnerability requires no credentials and no prior knowledge of the target instance beyond its URL.
Affected Versions
| Version Branch | Affected | Fixed In |
|---|---|---|
| v1.58.x | Yes | 0.58.24 |
| v1.59.x | Yes | 0.59.21 |
| v1.60.x | Yes | 0.60.17 |
| v1.61.x | Yes | 0.61.11 |
| v1.62.x | Yes | 0.62.9 |
| v1.63.x | Yes | 0.63.5 |
| Metabase Cloud | Yes — auto-patched | Applied Aug 6, 2026 |
Versions prior to v1.58 are not affected by this specific vulnerability.
Immediate Actions
1. Upgrade Now
Self-hosted Metabase operators must upgrade to the patched version for their branch immediately. Metabase Cloud was automatically patched on August 6 — cloud customers should verify their version in the admin panel.
2. Temporary Mitigation (If Patching Is Delayed)
Block access to the vulnerable endpoint at your reverse proxy or firewall:
# Nginx — block the vulnerable endpoint
location /api/session/reset_password {
    return 403;
}# Apache
<Location "/api/session/reset_password">
Deny from all
</Location>Note: Blocking this endpoint disables the password reset feature but prevents exploitation until patching is complete.
3. Post-Patch Remediation Steps
Metabase recommends the following after applying the patch:
-- Revoke all existing Metabase sessions (forces re-login for all users)
TRUNCATE TABLE core_session;Additionally:
- Rotate all database credentials for every database connected to your Metabase instance — assume they are compromised
- Audit Metabase admin accounts — verify no unauthorized accounts were created
- Review database access logs for unusual query patterns from Metabase's service account
- Check connected database permissions — limit Metabase's database user to read-only where possible
Why This Matters Beyond Metabase
Metabase is widely deployed as an analytics layer sitting on top of production databases. Unlike a standalone application breach, a Metabase compromise typically means the attacker has a pathway to every database the Metabase service account can reach — which in many organizations includes production customer databases, data warehouses, and internal reporting databases.
The Framework incident illustrates this clearly: customer PII was stolen not from Framework's primary production systems, but from an analytics integration that pulled from those systems.
Organizations should treat any BI/analytics tool with database access as high-value infrastructure, apply the principle of least privilege to its database connections, and maintain the same patching urgency as they would for production applications.
Note: Separate Metabase CVE Also Disclosed in July
A separate Metabase vulnerability — CVE-2026-59826 (CVSS 9.1) — was disclosed on July 9, 2026. That vulnerability allows an authenticated admin to execute arbitrary Java code via a malformed H2 database connection string. While less severe (requires admin credentials), it affects Metabase versions 1.55.0 through 1.58/1.59/1.60/1.61, and a public proof-of-concept exploit is available on GitHub. Organizations should ensure they are patched against both vulnerabilities.
Key Takeaways
- CVSS 10.0 zero-day — Unauthenticated SQL injection; no credentials needed
- Framework and Tally confirmed compromised on August 3, 2026
- Patch all self-hosted Metabase instances immediately — Cloud was auto-patched
- Rotate all connected database credentials — Assume they are stolen
- Block
/api/session/reset_passwordif unable to patch immediately - Treat BI tools as critical infrastructure — They often have production DB access
References
- BleepingComputer — Framework, Tally Disclose Metabase Data-Theft Attacks
- TechCrunch — Computer Maker Framework Notifies All Customers of a Data Breach
- Metabase Security Update Blog
- GitHub Advisory GHSA-vwf4-m7j8-wcjf
- Heise — Metabase Zero-Day: Data Leak at Framework
- SQ Magazine — Metabase Self-Hosted Patch Advisory