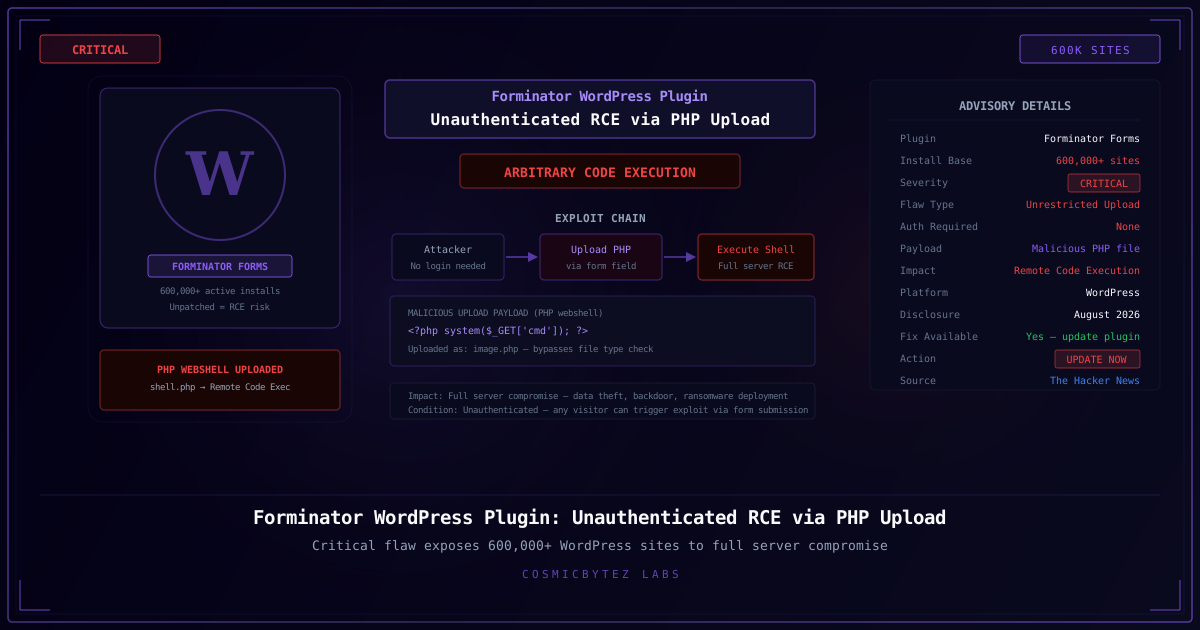
600,000+ WordPress Sites Exposed to Full Server Compromise
A critical security flaw has been disclosed in Forminator Forms, a WordPress plugin with more than 600,000 active installations, that allows unauthenticated attackers to upload malicious PHP files and achieve arbitrary code execution on susceptible servers. The vulnerability, tracked as CVE-2026-15748 with a CVSS score of 9.8, was patched in version 1.56.2 released on July 31, 2026.
Site administrators who have not yet updated are urged to do so immediately — with the Wordfence disclosure now public, exploitation attempts are considered imminent.
Vulnerability Details
| Field | Details |
|---|---|
| CVE | CVE-2026-15748 |
| CVSS Score | 9.8 (Critical) |
| Plugin | Forminator Forms |
| Affected Versions | All versions up to and including 1.56.1 |
| Fixed Version | 1.56.2 (released July 31, 2026) |
| Authentication Required | None |
| Discovered By | "daroo" (independent researcher) |
| Active Installations | 600,000+ |
Technical Analysis
Root Cause: Unrestricted File Upload
The flaw resides in the plugin's handle_file_upload() routine. The function fails to adequately validate uploaded file types before processing them, allowing unauthenticated users to submit arbitrary files — including executable .php files — to the server.
Exploitation Prerequisite
A specific configuration is required for exploitation: the target site must have a Forminator form that contains both a File Upload field and a Select field. When these conditions are met, there are no server-side restrictions preventing a malicious PHP webshell from being written to a web-accessible path.
Exploit Chain
Stage 1: Reconnaissance
└── Identify target site with Forminator form
    └── Confirm form has File Upload + Select field

Stage 2: Malicious Upload
└── Submit form with PHP webshell as the "file"
    └── handle_file_upload() fails to restrict .php extension
    └── Webshell written to web-accessible upload directory

Stage 3: Remote Code Execution
└── HTTP GET /wp-content/uploads/forminator/[upload]/shell.php?cmd=id
    └── Full server-side command execution achieved
    └── Complete site compromise — data theft, backdoor, ransomware
Example Payload
<?php system($_GET['cmd']); ?>Uploaded as shell.php (or any .php variant), this bypasses Forminator's file type check entirely. Once uploaded, the attacker can execute arbitrary system commands with the web server's privileges.
Companion Vulnerability
The same v1.56.2 patch also addresses CVE-2026-18325 (CVSS 7.2): an unauthenticated stored XSS via file upload — a separate attack vector with the same plugin version boundary.
Disclosure Timeline
| Date | Event |
|---|---|
| Pre-July 31, 2026 | Researcher "daroo" discovers and reports vulnerability |
| July 31, 2026 | Forminator 1.56.2 patch released |
| July 31 – Aug 18, 2026 | 18-day Wordfence embargo period; firewall rules pushed to Wordfence customers |
| August 17–18, 2026 | Public disclosure by Wordfence and The Hacker News |
Exploitation Risk Assessment
- No public PoC confirmed as of initial disclosure date
- Exploitation window is now open following public disclosure
- With 600,000+ installations and a zero-authentication requirement, mass scanning and automated exploitation is expected rapidly
- Wordfence customers received firewall rule coverage during the 18-day embargo — unprotected sites are now the primary target
Remediation
Immediate Action
Update Forminator Forms to version 1.56.2 or later immediately:
- In WordPress admin, navigate to Plugins → Installed Plugins
- Find Forminator and click Update Now
- Verify the active version shows 1.56.2 or higher
Verify Your Form Configuration
If you cannot update immediately:
- Disable or remove all forms that contain both a File Upload field and a Select field
- Alternatively, remove the File Upload field from all affected forms as a temporary mitigation
Secondary Defenses
- Enable WAF protection — Wordfence, Cloudflare WAF, or similar
- Review uploaded files directory (
/wp-content/uploads/forminator/) for unexpected PHP files - Restrict PHP execution in upload directories via
.htaccess:<FilesMatch "\.php$"> Deny from all </FilesMatch> - Monitor web server access logs for requests to upload directories
Why This Vulnerability Is Serious
Unauthenticated file upload flaws on popular WordPress plugins represent a particularly dangerous class of vulnerability because:
- Mass exploitation is trivial — automated scanners can identify vulnerable sites at scale
- No skill required — a basic webshell is sufficient for full compromise
- 600,000+ sites means even a small exploitation rate affects tens of thousands of sites
- Post-compromise impact is severe — ransomware deployment, data theft, SEO spam, and credential harvesting are all common follow-on attacks
Sources
- The Hacker News — Forminator WordPress Flaw Can Enable Unauthenticated RCE
- CyberSecurityNews — Critical WordPress Plugin Vulnerability Exposes 600,000+ Sites
- Wordfence — Forminator Plugin Vulnerability Intelligence