A Refinement, Not an Overhaul
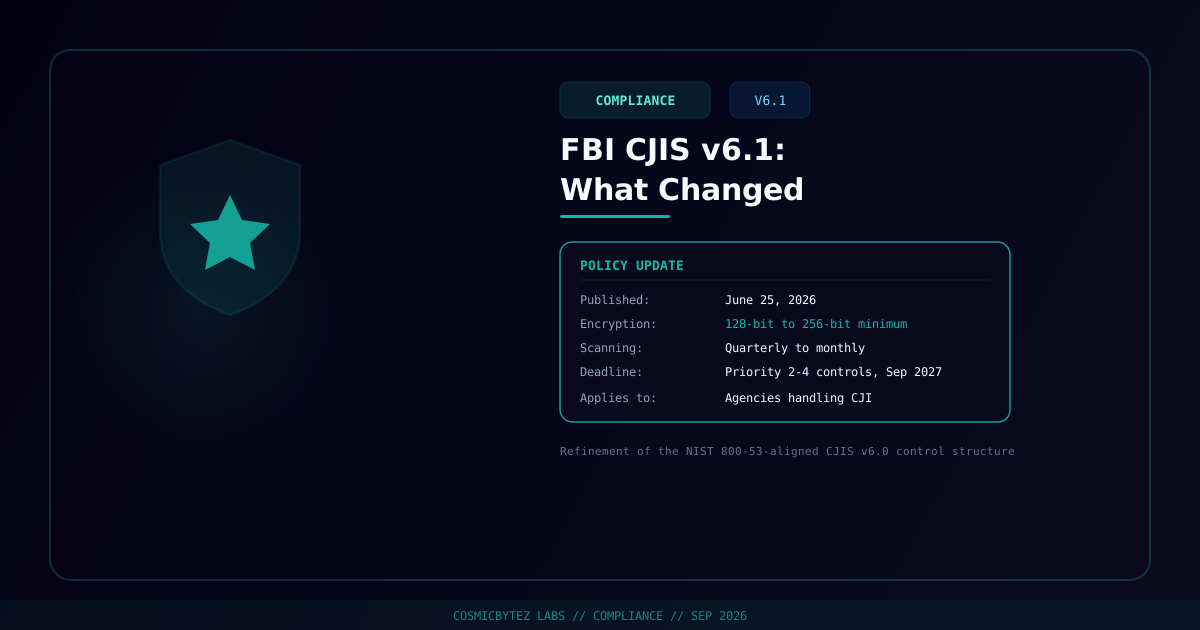
The FBI has published version 6.1 of its Criminal Justice Information Services (CJIS) Security Policy, dated June 25, 2026. It's a refinement of the modernized v6.0 framework rather than a wholesale rewrite — v6.0 had already moved CJIS toward a control-based structure closely aligned with NIST SP 800-53, and v6.1 tightens specific technical requirements within that same structure.
What Changed
Encryption requirements increased across the board. Both data-in-transit and data-at-rest encryption must now use at least 256-bit strength, up from the previous 128-bit minimum. Agencies still running systems configured for 128-bit encryption will need to plan upgrades.
Vulnerability scanning frequency doubled. Security update and firmware vulnerability assessments must now happen at least monthly, replacing the previous quarterly cadence — a meaningful increase in operational burden for smaller agencies without dedicated vulnerability management tooling.
MFA and password requirements are unchanged. Multi-factor authentication remains mandatory for both privileged and non-privileged accounts, and agencies must still maintain and check passwords quarterly against lists of commonly used, expected, or previously compromised passwords.
Compliance Timeline
CJIS uses a tiered enforcement model. Priority 1 controls have been sanctionable since October 1, 2024. Priority 2 through 4 controls remain in "zero-cycle" status — meaning they're documented but not yet enforced — until September 30, 2027, giving agencies a multi-year runway to reach full compliance on the lower-priority items.
Who Needs to Care
CJIS Security Policy compliance applies to any law enforcement or criminal justice agency — and their vendors and contractors — that handles Criminal Justice Information (CJI). That includes state and local police departments, court systems, and any private-sector partner (cloud hosting, records management, forensic tooling) that touches CJI on an agency's behalf. Compliance is typically verified through state CJIS Systems Agency audits.
Why This Matters
The 256-bit encryption bump and monthly scanning requirement are the two changes worth acting on now, not waiting for the 2027 zero-cycle deadline to force the issue. Security teams supporting law enforcement or justice-system customers should audit current encryption configurations against the new minimum and confirm their vulnerability scanning cadence actually meets "at least monthly" in practice, not just on paper — CJIS audits have historically been unforgiving about the gap between documented policy and demonstrated practice.