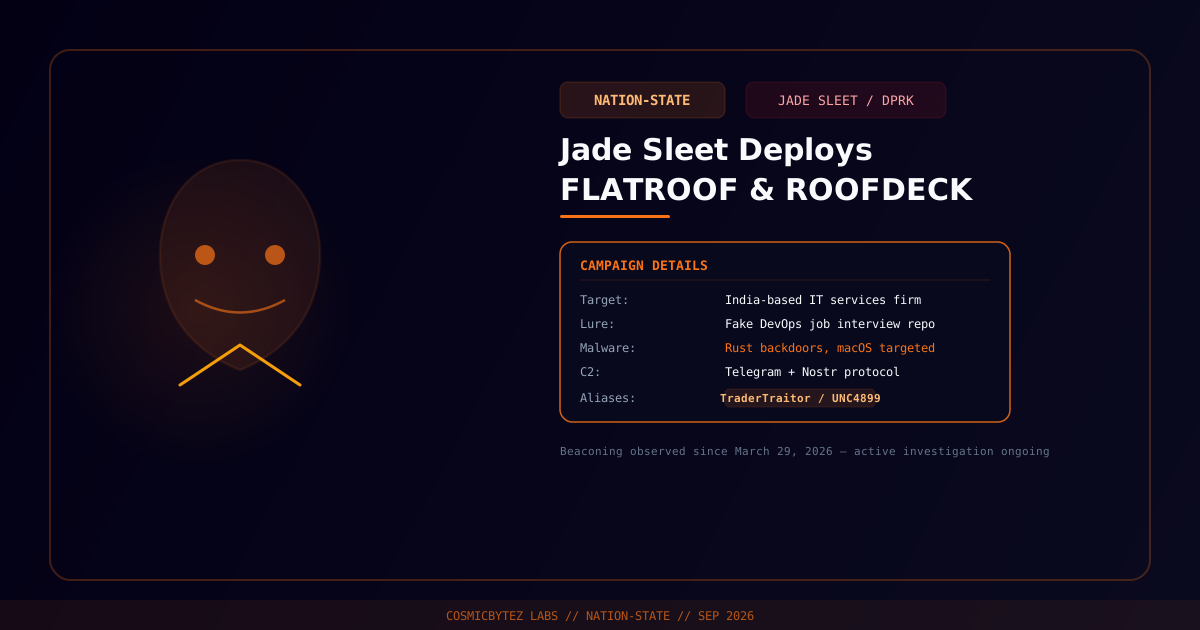
Fake Job Interview, Real Backdoor
Jade Sleet — the North Korean state-sponsored threat actor also tracked as PUKCHONG, Slow Pisces, TraderTraitor, and UNC4899 — has been linked to the compromise of an India-based IT services company, according to new research. The intrusion began on the workstation of a DevOps engineer running Apple Silicon, and backdoor activity was detectable as early as March 18, 2026, with active command-and-control beaconing starting March 29.
The initial access vector follows Jade Sleet's well-worn playbook: a fake job interview lure aimed at developers. The victim was drawn into a coding exercise built around a project repository styled as terraform-candidate-repo, weaponized with a malicious .terraform.lock.hcl dependency lock file pointing to attacker-controlled domains instead of the legitimate Terraform registry.
Two New Rust Backdoors
The campaign deployed two previously catalogued Rust-based macOS backdoors:
| Backdoor | C2 Channel | Capabilities |
|---|---|---|
| FLATROOF (aka Gaslight) | Telegram | Command execution, file theft, browser data and system info harvesting |
| ROOFDECK | Nostr protocol (decentralized) | Remote shell, file manipulation, persistence via Launch Agents |
Using Telegram and the decentralized Nostr protocol for command-and-control lets the operators blend into normal application traffic and sidesteps single-point-of-failure C2 infrastructure that defenders could otherwise sinkhole.
Investigators traced attacker activity into the compromised engineer's own workspace — specifically a ~/DevOps-Automation/cloudshield directory accessed through the Cursor AI code editor — suggesting the intrusion may have pivoted through, or at least touched, developer tooling rather than staying confined to a single terminal session.
Why This Matters
Jade Sleet has spent the past several years refining a single core technique — social-engineering developers, particularly those working in DevOps, cryptocurrency, or fintech roles, with fake recruiting and coding-challenge lures — into a reliable initial-access method for supply chain intrusions. This incident is notable less for novelty and more for reach: it confirms the group continues actively targeting IT services providers in South Asia, expanding well beyond its historically North America- and Europe-heavy target list, and continues investing in macOS-native tooling as Apple Silicon adoption grows among the developer population it targets.
Organizations with DevOps, SRE, or platform engineering staff should treat unsolicited coding-challenge repositories — especially ones bundling Terraform, Docker, or other infrastructure-as-code dependency files — as a credible initial-access vector, not just a phishing nuisance.
Recommendations
- Review Terraform and other IaC lock files in any repository provided by an external party before running
terraform initor equivalent — verify registry URLs match expected sources - Isolate coding-challenge and interview-exercise environments from production credentials and developer SSH/API keys, ideally in a disposable VM or container
- Monitor for anomalous Telegram or unusual outbound protocol traffic (including Nostr relay connections) from developer endpoints
- Audit Launch Agent persistence on macOS developer machines for unrecognized entries
- Treat AI-assisted code editors (Cursor and similar) as part of the attack surface — review their access logs alongside standard EDR telemetry during incident response