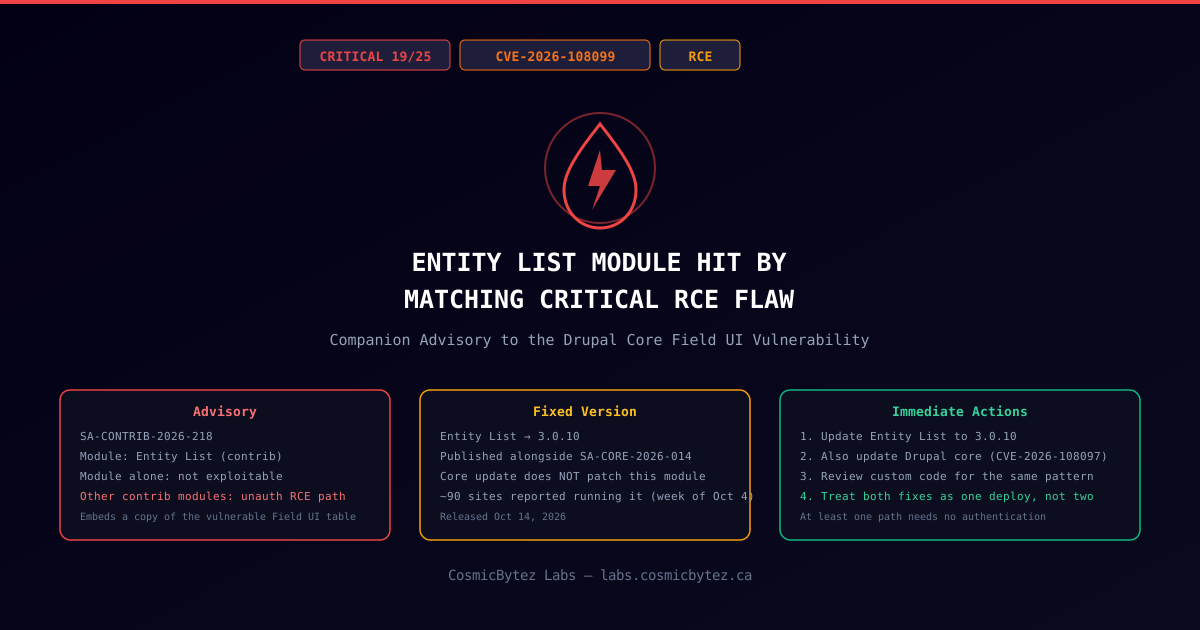
Entity List Module Ships a Companion Critical RCE Fix
Two days after the Drupal Security Team patched a critical remote code execution flaw in core's Field UI module (CVE-2026-108097, SA-CORE-2026-014), the team has shipped a matching critical advisory for the Entity List contributed module, tracked as CVE-2026-108099 and documented in SA-CONTRIB-2026-218. Both advisories carry the same 19/25 "Critical" risk rating on Drupal's internal scale, and for good reason: Entity List embeds its own copy of the same vulnerable Field UI table-rendering code, patched in an identical way in its 3.0.10 release.
Entity List is a contributed module that lets site builders create lists of entities without needing the full Views module. As with the core flaw, the module alone is not directly exploitable — but the advisory warns that "multiple serious exploit paths exist with other contributed modules," and at least one known path requires no authentication at all. Custom code that touches the same rendering logic can expose the bug too.
Vulnerability Details
| Attribute | Value |
|---|---|
| CVE ID | CVE-2026-108099 |
| Advisory | SA-CONTRIB-2026-218 |
| Risk Score | 19/25 (Critical) — same Drupal risk formula as the related core advisory; no standard CVSS vector published |
| Vulnerable Component | Entity List module — a contributed module for building entity lists without Views |
| Root Cause | Entity List embeds a copy of Field UI's vulnerable pre-render logic, inheriting the same unchecked call_user_func_array issue |
| Attack Vector | Not exploitable through the module alone; requires another contributed module or custom code exposing the vulnerable path; at least one known contrib-module path needs no authentication |
| Fixed Version | Entity List 3.0.10 |
| Related Advisory | SA-CORE-2026-014 / CVE-2026-108097 (Drupal core, Field UI module) |
| Release Window | October 14, 2026, published alongside the core advisory |
| Exploitation Status | No confirmed in-the-wild exploitation at disclosure; same "exploits might be developed within hours or days" warning as the core flaw |
| Reported Adoption | Approximately 90 sites reported running Entity List in the week starting October 4, 2026 |
Why a Separate Advisory for the Same Bug
Drupal's core and contributed-module ecosystems are patched independently — updating Drupal core to 11.4.10, 11.3.19, or 10.6.19 does not touch code shipped inside a contributed module, even if that module copy-pasted a vulnerable core table. Entity List's release notes for 3.0.10 confirm the fix "mirrors the Field UI change," meaning site operators who only applied the core update are still exposed through Entity List until they separately update the module itself.
This is a useful reminder for any Drupal site maintainer: a core security release does not guarantee your contributed modules are safe, especially when those modules vendor or duplicate core functionality for their own rendering needs.
Who Is Affected
- Sites running the Entity List module below version 3.0.10, regardless of whether Drupal core has already been patched for CVE-2026-108097
- Sites combining Entity List with other contributed modules or custom code that exposes an unauthenticated path into the shared vulnerable rendering logic
- Given the module's modest adoption (~90 sites as of early October), this is a smaller blast radius than the core Field UI advisory, but no less critical for affected sites
Mitigation
Immediate Actions
- Update the Entity List module to 3.0.10 or later. Treat this as a separate deployment step from the Drupal core update — one does not substitute for the other.
- Also apply the Drupal core fix (11.4.10, 11.3.19, or 10.6.19, per your branch) for CVE-2026-108097 if you haven't already; the two advisories address the same underlying class of bug in different codebases.
- If you cannot update Entity List immediately, consider temporarily disabling the module, mirroring the core advisory's guidance to uninstall Field UI as an interim measure.
Detection and Defence-in-Depth
- Audit any custom code that interacts with Entity List's or Field UI's rendering paths for the same unchecked
call_user_func_arraypattern described in SA-CORE-2026-014. - Review which contributed modules are installed alongside Entity List, since the exploit path specifically depends on module combinations rather than Entity List in isolation.
- Drupal Steward coverage for the core advisory does not automatically extend to every contributed-module variant of the bug — confirm with your hosting or security vendor whether Entity List is covered.
Background
Entity List gives Drupal site builders a lighter-weight way to generate lists of entities (nodes, users, taxonomy terms, etc.) without configuring the full Views module. Because it reimplements some of Field UI's table-rendering behavior internally rather than calling into core, it inherited the same vulnerability pattern — illustrating how vulnerable code can quietly propagate into the contributed-module ecosystem even when the original flaw is fixed at the source.