Executive Summary
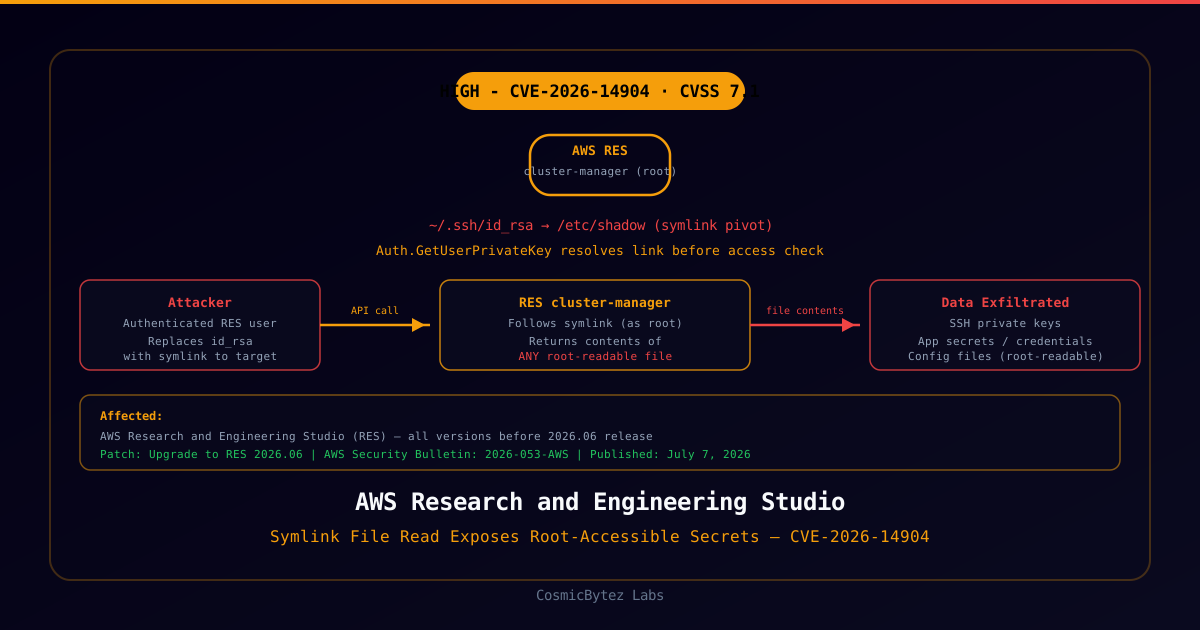
CVE-2026-14904 is a high-severity path traversal via symlink (CWE-59) vulnerability in AWS Research and Engineering Studio (RES). The Auth.GetUserPrivateKey API resolves symbolic links before checking file access permissions, and the cluster-manager service that processes these requests runs as root. An authenticated attacker can replace their own SSH private key file with a symbolic link pointing to any file accessible by root — including other users' SSH private keys, application credentials, and environment configuration secrets.
| Attribute | Value |
|---|---|
| CVE ID | CVE-2026-14904 |
| CVSS Score | 7.1 (High) |
| CVSS Vector | CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:N/VA:N |
| CWE | CWE-59 — Improper Link Resolution Before File Access |
| Authentication | Low privilege (valid RES account required) |
| Attack Vector | Network |
| Impact | Confidentiality — High |
| AWS Bulletin | 2026-053-AWS |
| Published | July 7, 2026 |
| CISA KEV | No |
Vulnerability Overview
Root Cause
AWS Research and Engineering Studio exposes the Auth.GetUserPrivateKey API, which is designed to return a user's SSH private key from their home directory (~/.ssh/id_rsa). The vulnerability exists because:
- The API resolves symbolic links before enforcing file access restrictions
- The cluster-manager process that services this API call executes as root
- There is no check to ensure the resolved path remains within the user's home directory
This combination allows an authenticated user to create a symlink from their expected key path to any target file on the filesystem, causing the cluster-manager to return the target file's contents as if it were their SSH key.
Attack Path
1. Attacker authenticates to RES with a valid (low-privilege) account
2. Attacker replaces ~/.ssh/id_rsa with a symlink:
   ln -s /etc/shadow ~/.ssh/id_rsa
   (or target any credential file, config, or root-readable secret)
3. Attacker calls Auth.GetUserPrivateKey via the RES API
4. cluster-manager (running as root) follows the symlink
5. Contents of /etc/shadow (or target file) returned to attacker
What Can Be Exfiltrated
Because the cluster-manager runs as root, any file readable by root is a potential target:
- Other users' SSH private keys (
~/.ssh/id_rsafor any user) - Application secrets and credentials stored in environment files
- Database connection strings embedded in configuration files
- AWS credential files (
~/.aws/credentials) - System password hashes (
/etc/shadow) - Private TLS certificates and keys
Affected Products
| Product | Affected Versions | Fixed Version |
|---|---|---|
| AWS Research and Engineering Studio (RES) | All versions before 2026.06 | 2026.06 |
AWS Research and Engineering Studio is a managed service that enables researchers and engineers to provision and manage HPC clusters, virtual desktops, and collaborative computing environments on AWS.
Remediation
Patch
Upgrade to AWS RES version 2026.06 or later. This is the only documented remediation. AWS has not published additional interim workarounds.
Verify Your Version
# Check your current RES deployment version via AWS Console:
# Navigate to AWS RES → Settings → About

# Or via AWS CLI:
aws res get-cluster-info --query 'ClusterInfo.SoftwareVersion'Post-Upgrade Actions
If you were running an affected version of RES, consider the following:
- Audit
Auth.GetUserPrivateKeyAPI call logs — Review CloudTrail logs for unusual calls to this API from unexpected users or at unusual times - Rotate potentially exposed credentials — If any user could have exploited this, rotate all SSH keys, AWS credentials, and application secrets accessible on the cluster-manager host
- Audit file system for unexpected symlinks — Check user home directories for symlinks that point outside the home directory
# Find symlinks in user home directories pointing outside /home
find /home -type l -exec sh -c 'target=$(readlink -f "$1"); [[ "$target" != /home/* ]] && echo "Suspicious symlink: $1 -> $target"' _ {} \;Detection
CloudTrail Log Review
Monitor AWS CloudTrail for GetUserPrivateKey API calls and correlate against expected user activity:
| Signal | Description |
|---|---|
GetUserPrivateKey calls from service accounts | Unexpected callers |
High-frequency GetUserPrivateKey calls | Possible scanning/enumeration |
| Calls at unusual hours | Off-hours exploitation attempts |
File System Indicators
| Indicator | Description |
|---|---|
Symlinks in ~/.ssh/ pointing outside home dir | Exploitation setup |
| Unexpected file reads in audit logs for sensitive paths | Successful exploitation |
Modified ~/.ssh/id_rsa mtime without corresponding key rotation | Possible symlink swap |
Context: AWS RES Architecture
AWS Research and Engineering Studio is deployed with a cluster-manager EC2 instance that orchestrates resources. This component runs privileged processes that interact with user home directories shared across the cluster. The privileged execution context — necessary for cluster management functions — is what enables this vulnerability to read files beyond the intended scope.
The pattern of "privileged service following user-controlled symlinks" is a class of vulnerability (CWE-59 / TOCTOU) that appears across many HPC and shared computing systems. Defenders should review any service that:
- Runs as root or a highly privileged user
- Accesses files based on user-controlled paths
- Does not canonicalize paths before access
Key Takeaways
- CVSS 7.1 High — Authenticated users can read any root-accessible file via symlink pivot
- AWS RES cluster-manager runs as root — Dramatically expands the impact of the path traversal
- Upgrade to RES 2026.06 — The only published remediation
- Audit CloudTrail for
Auth.GetUserPrivateKeycalls if running an affected version - Rotate all secrets on affected clusters — SSH keys, AWS credentials, application config secrets