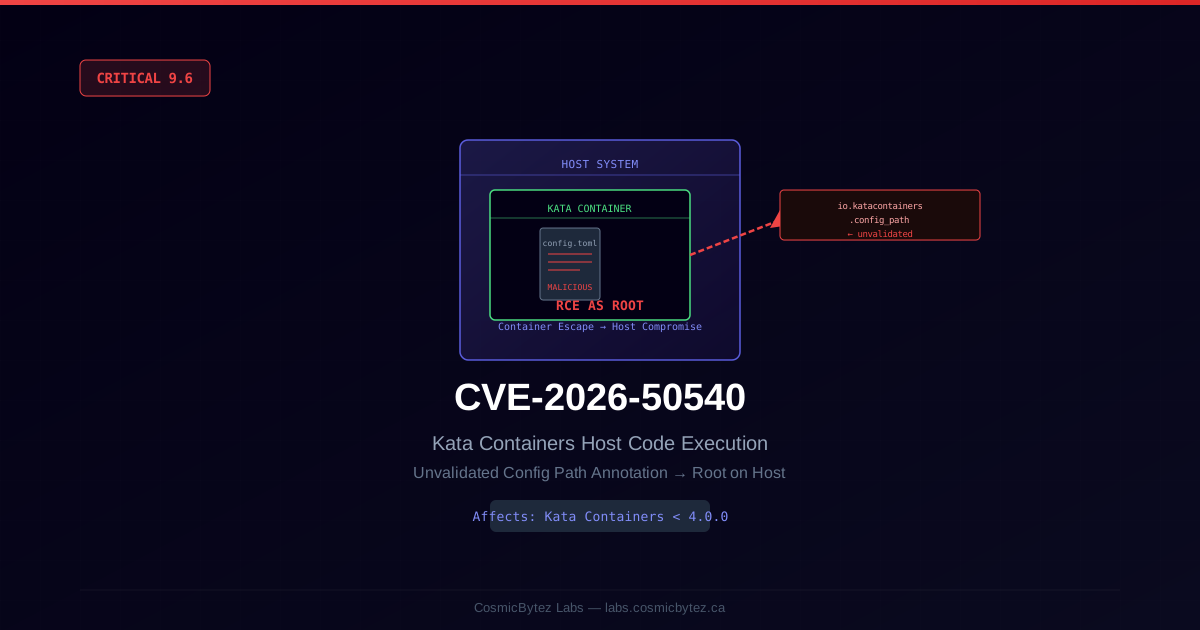
Overview
A critical remote code execution vulnerability has been disclosed in Kata Containers, the open-source project that implements lightweight virtual machines designed to run like containers. Tracked as CVE-2026-50540 with a CVSS v3.1 score of 9.6 (Critical), the flaw allows an attacker with pod-level access to escape the container boundary and execute arbitrary code as root on the underlying host system.
The vulnerability was published on August 7, 2026 and has been assigned by GitHub Security Advisory (GitHub_M CNA). Organizations running Kata Containers in Kubernetes or other container orchestration environments should treat this as an emergency patching priority.
Vulnerability Details
The root cause lies in how kata-runtime handles the io.katacontainers.config_path pod annotation. This annotation instructs the runtime to load an alternative configuration file from the host filesystem — and critically, the path and contents of this file are accepted without any validation or restriction.
An attacker who has already gained access to a running pod can exploit this behavior by:
- Crafting a malicious TOML configuration file that points to an attacker-controlled binary or script
- Setting the
io.katacontainers.config_pathpod annotation to reference that file - Triggering the runtime to load the malicious config
- Achieving code execution as root on the host — outside the container sandbox
This constitutes a scope change from pod to host, which is reflected in the CVSS vector AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:N.
CVSS Breakdown
| Metric | Value |
|---|---|
| Base Score | 9.6 Critical |
| Attack Vector | Network |
| Attack Complexity | Low |
| Privileges Required | Low |
| User Interaction | None |
| Scope | Changed |
| Confidentiality | High |
| Integrity | High |
| Availability | None |
Affected Products
| Product | Affected Versions | Fixed Version |
|---|---|---|
| Kata Containers (kata-runtime) | All versions prior to 4.0.0 | 4.0.0 |
Impact
Successful exploitation results in:
- Container escape: The attacker breaks out of the Kata Containers VM sandbox
- Root-level code execution on the host: Full compromise of the underlying node
- Scope change: From a single pod to the hypervisor host, potentially affecting all co-located workloads
- Lateral movement: From the compromised host, attackers can pivot to other nodes in the cluster
In multi-tenant Kubernetes environments — particularly cloud provider infrastructure — this vulnerability could have severe cascading impact.
Remediation
Immediate Action
Upgrade to Kata Containers 4.0.0 or later. This release introduces proper validation of the io.katacontainers.config_path annotation, rejecting arbitrary host file paths and enforcing content restrictions.
# Verify your current Kata Containers version
kata-runtime --version

# Follow your distribution's upgrade path to >= 4.0.0
# For containerd-based deployments:
# https://github.com/kata-containers/kata-containers/releasesWorkarounds
If immediate upgrade is not possible:
- Restrict pod annotation permissions via Kubernetes admission webhooks (OPA Gatekeeper, Kyverno) to deny the
io.katacontainers.config_pathannotation on all pods - Limit pod deployment permissions to trusted users and service accounts only
- Enable audit logging for pod annotation changes to detect attempted exploitation
Detection
Look for unusual process trees originating from the Kata Containers runtime, particularly:
- Unexpected binaries spawned by
kata-runtimeorcontainerd-shim-kata-v2 - Host-level file writes from container PID namespaces
- Unusual TOML files placed in world-writable directories
Review pod annotation logs for any use of the io.katacontainers.config_path key on production workloads.