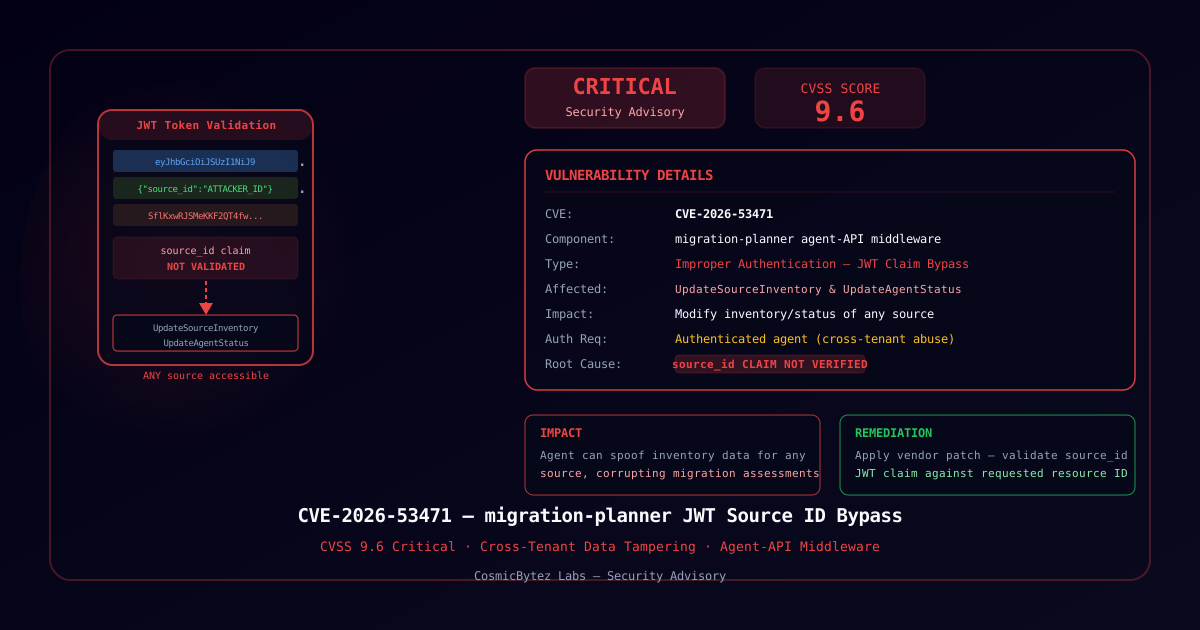
Executive Summary
CVE-2026-53471 is a critical improper authentication vulnerability (CVSS 9.6) affecting migration-planner, Red Hat's migration planning tool for OpenShift and Kubernetes. The agent-API middleware processes JSON Web Tokens (JWTs) for authentication but fails to validate the source_id claim within those tokens against the requested source ID in the UpdateSourceInventory and UpdateAgentStatus handlers. As a result, an authenticated agent can submit inventory updates or status changes for any source in the system — not just the one it is legitimately associated with — enabling cross-tenant data tampering and potentially corrupted migration assessments.
Vulnerability Details
| Field | Details |
|---|---|
| CVE | CVE-2026-53471 |
| CVSS Score | 9.6 (Critical) |
| Type | Improper Authentication — JWT Claim Validation Failure (CWE-287) |
| Component | migration-planner — agent-API middleware |
| Affected Handlers | UpdateSourceInventory, UpdateAgentStatus |
| Authentication Required | Yes (any authenticated agent) |
| Attack Vector | Network |
| Impact | Cross-tenant inventory data tampering, corrupted assessments |
| Published | 2026-06-10 |
Technical Analysis
How migration-planner Agent Authentication Works
migration-planner deploys agents to source environments that report back discovered inventory data. These agents authenticate to the API using JWTs, which contain claims including a source_id field identifying which source the agent belongs to. The API middleware is responsible for authenticating these JWTs and authorizing agents to update only their associated source data.
Root Cause
The agent-API middleware correctly processes JWTs and validates the signature, but the UpdateSourceInventory and UpdateAgentStatus handlers fail to compare the source_id claim in the JWT against the source_id parameter specified in the API request. This means the middleware verifies that a JWT exists and is valid, but not which source that JWT authorizes the agent to modify.
Agent JWT: { ..., "source_id": "agent-own-source-id", ... }

POST /api/v1/sources/ANY_SOURCE_ID/inventory
  ↓
Middleware: JWT valid? ✓ (but source_id claim not checked against path param)
  ↓
UpdateSourceInventory handler: Updates source ANY_SOURCE_ID
  ↓
Result: Attacker agent modifies inventory of victim source
Attack Scenario
An attacker who controls a migration-planner agent (even a legitimately provisioned one) can:
- Obtain a valid JWT for their own source ID through normal authentication
- Send
UpdateSourceInventoryorUpdateAgentStatusrequests targeting a different source ID in the path or body - The middleware validates the JWT signature but never checks that the
source_idin the JWT matches the target source - The handler processes the request as if the agent is authorized for the victim source
This allows the attacker to:
| Action | Impact |
|---|---|
| Poison inventory data | Corrupt migration readiness assessments for other tenants |
| Falsify agent status | Make healthy sources appear as problematic or vice versa |
| Disrupt migration planning | Cause incorrect decisions about migration feasibility |
| Persistent data corruption | Tampered assessments may persist and affect downstream decisions |
Why CVSS 9.6?
The high score reflects that a valid JWT from any legitimate source context can be used to modify arbitrary cross-tenant data, there is no secondary control preventing the abuse, and the integrity impact on migration assessment data is complete.
Affected Environments
Deployments of migration-planner that:
- Use JWT-based agent authentication
- Have multiple agents or tenants
- Run the affected handlers (
UpdateSourceInventory,UpdateAgentStatus) - Have not applied the vendor patch
Remediation
Immediate Action
Apply the vendor patch from Red Hat. The patch adds source_id claim validation to both affected handlers, verifying that the source_id embedded in the agent's JWT matches the source ID being targeted in the API request before processing any update.
The corrected flow:
JWT.source_id == request.source_id? → YES → proceed
                                    → NO  → 403 Forbidden
Compensating Controls (Pre-Patch)
- Restrict agent network access — Limit agents to only being able to reach the migration-planner API from their own source environment using network policies or firewall rules
- Audit agent JWT issuance — Verify that JWTs are issued to agents with the correct
source_idand that those tokens are not transferable between environments - Monitor for cross-source updates — Log and alert on any agent sending inventory updates for a source ID different from the one in its JWT
Post-Patch Steps
- Audit inventory data integrity — Review migration assessment data for unexpected changes that may indicate prior exploitation
- Re-run affected assessments — For any tenants whose data may have been tampered with, trigger fresh inventory collection to restore accurate data
- Review agent provisioning — Ensure each agent is provisioned with a JWT bound to its own
source_idand that agents cannot be easily moved between environments
Detection
# Look for UpdateSourceInventory or UpdateAgentStatus requests
# where the source_id in the path/body differs from the authenticated agent
# (requires application-layer logging with JWT claim context)

# In API logs, flag requests where the JWT source_id != path source_id
grep 'UpdateSourceInventory\|UpdateAgentStatus' /var/log/migration-planner/app.log | \
  grep -v 'source_id_match=true'

# Monitor for unusual patterns: one agent updating multiple different source IDsSigns of exploitation include:
- Inventory data that has changed without corresponding agent activity from the owning environment
- Assessment results that conflict with known infrastructure state
- Log entries showing agents targeting source IDs other than their own