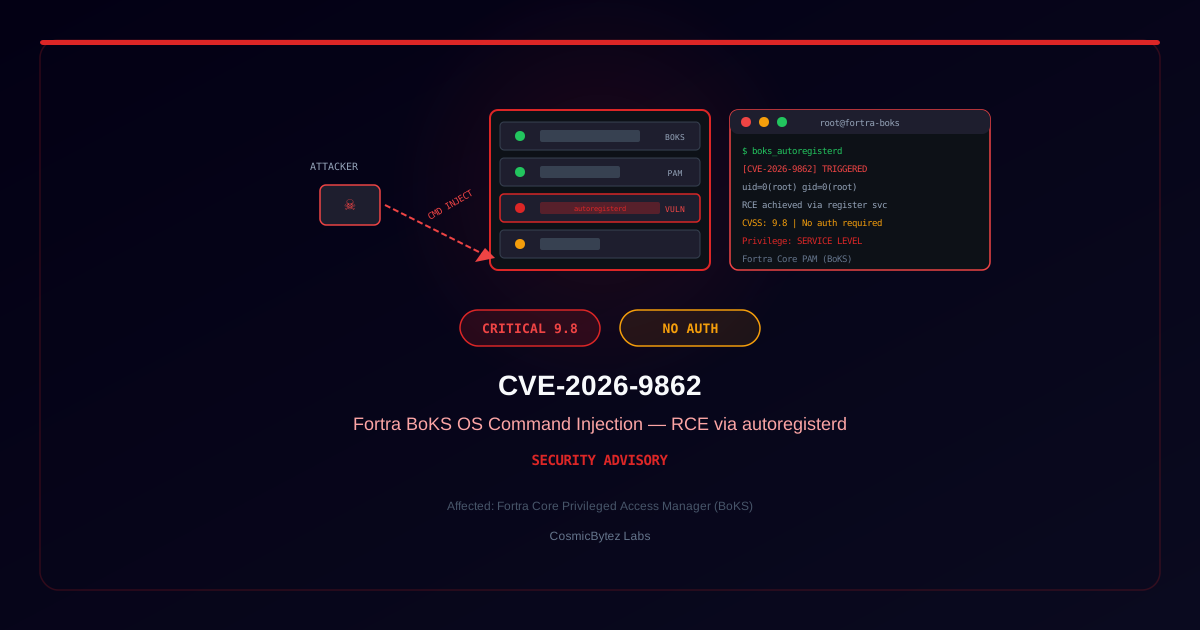
Critical OS Command Injection in Fortra BoKS PAM
CVE-2026-9862 is a critical-severity OS command injection vulnerability in Fortra's Core Privileged Access Manager (BoKS). A remote attacker with network access to the boks_autoregisterd service can inject arbitrary OS commands that execute with the privileges of the service — without any authentication required.
| Field | Detail |
|---|---|
| CVE ID | CVE-2026-9862 |
| CVSS Score | 9.8 (Critical) |
| Attack Vector | Network |
| Privileges Required | None |
| User Interaction | None |
| Affected Product | Fortra Core Privileged Access Manager (BoKS) |
| Vulnerable Component | boks_autoregisterd service |
| Published | 2026-06-15 |
Vulnerability Details
The boks_autoregisterd service in Fortra BoKS handles autoregistration of new hosts and endpoints. Due to insufficient input sanitization, user-supplied data passed to this service during the autoregistration process is directly interpreted by the underlying operating system shell.
An unauthenticated attacker with network-level access to the affected service port can inject OS commands as part of a crafted registration request. These commands execute with the privileges of the boks_autoregisterd service, which typically runs with elevated system permissions in PAM deployments.
Attack Flow
- Discovery — Attacker scans for BoKS autoregisterd service ports on corporate networks
- Crafted request — Sends a malicious autoregistration request containing shell metacharacters
- Command execution — Injected commands run with service-level privileges on the BoKS server
- Lateral movement — Attacker leverages PAM server access to pivot to managed privileged accounts
Impact
Fortra BoKS is an enterprise Privileged Access Management (PAM) solution. Successful exploitation of this vulnerability grants an attacker:
- Remote code execution on the BoKS server without credentials
- Access to PAM infrastructure that typically manages root/admin credentials across the enterprise
- Potential for complete network takeover — PAM servers are high-value targets with access to thousands of privileged accounts
Because PAM solutions sit at the heart of enterprise access control, compromise of a BoKS server is equivalent to gaining the keys to the kingdom for all managed systems.
Affected Versions
Consult the NVD entry for CVE-2026-9862 and Fortra's official security advisory for specific version ranges and patch availability.
Remediation
- Apply vendor patches immediately — Monitor Fortra's security advisory portal for patch releases
- Restrict network access — Firewall the
boks_autoregisterdport to authorized hosts only - Monitor for exploitation — Review logs for unexpected process spawning from the autoregisterd service
- Audit BoKS configurations — Review which hosts are permitted to autoregister
Detection
Watch for anomalous child processes spawned by boks_autoregisterd, unexpected outbound connections from the BoKS server, or unusual entries in the BoKS audit log around registration events.
References
- NVD — CVE-2026-9862
- Fortra Security Advisory (see vendor portal)