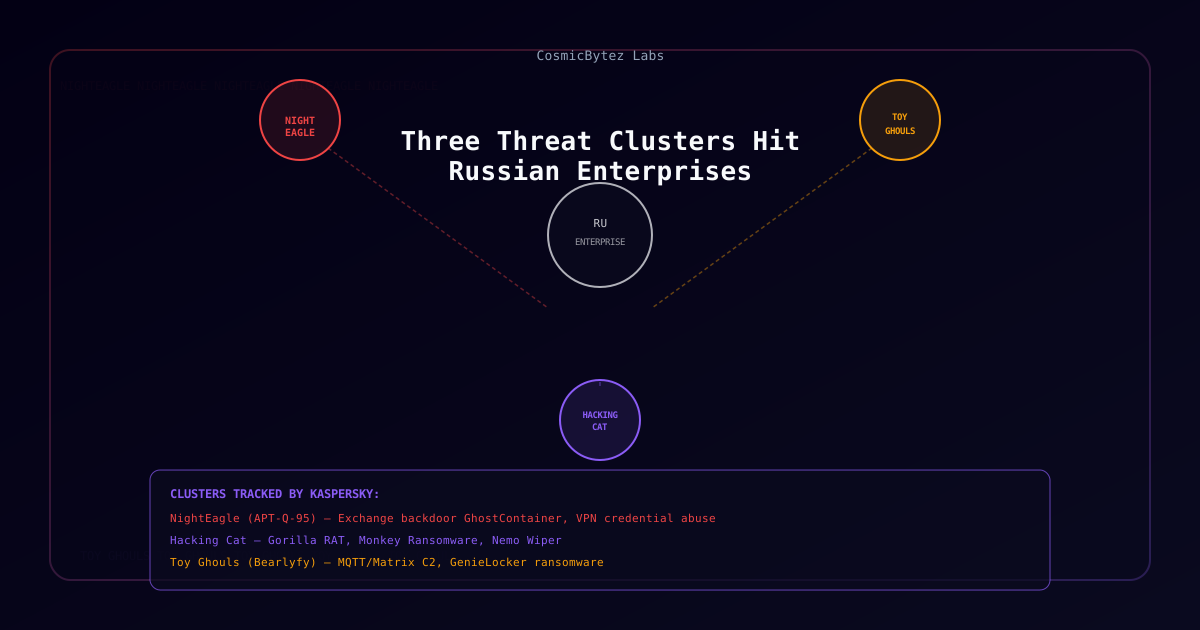
Three Distinct Clusters, One Target Population
Kaspersky researchers have published new findings on three separate threat activity clusters — tracked as NightEagle, Hacking Cat, and Toy Ghouls — all currently targeting enterprises in Russia, but with markedly different origins, tooling, and objectives. The report underscores that Russian organizations are being squeezed from multiple directions at once: state-aligned espionage, pro-Ukraine hacktivism, and financially motivated cybercrime.
CosmicBytez Labs has previously covered Hacking Cat's evolution toward destructive tooling in detail — this piece focuses on the two newly documented clusters, NightEagle and Toy Ghouls.
NightEagle (APT-Q-95): Long-Running Espionage
NightEagle, also tracked as APT-Q-95, has been active against Russian targets since at least 2023. Kaspersky describes a patient, infrastructure-focused operator rather than a smash-and-grab crew.
| Field | Details |
|---|---|
| Also known as | APT-Q-95 |
| Active since | At least 2023 |
| Initial access | Compromised VPN credentials routed through Cloudflare WARP tunnels and European VPN providers |
| Exploited flaws | CVE-2019-0708 (BlueKeep), Active Directory vulnerabilities |
| Lateral movement | Microsoft Dev Tunnels, rdp2tcp |
| Primary malware | GhostContainer — modular backdoor targeting Exchange servers |
| Notable components | Incorporates Neo-reGeorg tunneling and ysoserial deserialization tooling |
| Objective | Persistence, privilege escalation, domain controller compromise |
GhostContainer's design — a modular backdoor built specifically to nest inside Exchange server infrastructure — points to an operator prioritizing long-term, low-noise access over immediate disruption. The reuse of BlueKeep, a six-year-old RDP vulnerability, alongside living-off-the-land tools like Microsoft's own Dev Tunnels feature, suggests NightEagle leans on well-worn techniques that remain effective simply because patching and hardening lag in target environments.
Toy Ghouls (Bearlyfy): From Leaked Builders to Custom Tooling
Toy Ghouls — also referred to as Bearlyfy, Laboo.boo, or Feral Wolf across different tracking — represents a newer but fast-evolving entrant, active since 2025, with its first custom-built backdoor observed in July 2026.
| Field | Details |
|---|---|
| Aliases | Bearlyfy, Laboo.boo, Feral Wolf |
| Active since | 2025 |
| First custom backdoor observed | July 2026 |
| Delivery method | WinRM, using Evil-WinRM and WinRM-fs tooling |
| C2 channels | mqtt-bird-agent (via HiveMQ MQTT broker), matrix-bird-agent (via Element/Matrix messenger) |
| Ransomware | GenieLocker |
| Notable evolution | Moved from leaked ransomware builders to purpose-built tools |
The use of legitimate messaging and IoT protocols — MQTT and Matrix — as command-and-control channels is a deliberate evasion choice: traffic to a commercial MQTT broker or a Matrix homeserver blends into normal enterprise network noise far more easily than a bespoke C2 protocol would, complicating detection for defenders relying on signature- or destination-based blocking.
Why This Matters
Kaspersky's grouping of NightEagle, Hacking Cat, and Toy Ghouls under one report illustrates a broader pattern: Russian enterprises currently face simultaneous pressure from state-aligned espionage actors, pro-Ukraine hacktivist collectives, and financially motivated crews, each with distinct tradecraft but occasionally overlapping techniques (Exchange-server exploitation, in particular, shows up across more than one cluster). For defenders, that means threat models built around a single adversary type — "just ransomware" or "just APT" — are increasingly incomplete. Overlapping tool reuse and shared initial-access techniques (VPN credential abuse, Exchange exploitation, living-off-the-land lateral movement) also complicate attribution, a challenge Kaspersky notes explicitly in its Hacking Cat findings and one that likely applies across all three clusters.
Defensive Takeaways
- Patch Exchange and legacy RDP exposure — both NightEagle's BlueKeep reuse and Hacking Cat's Exchange exploitation rely on issues with patches long available.
- Monitor for anomalous outbound MQTT/Matrix traffic — Toy Ghouls' use of commodity messaging protocols for C2 is a detection opportunity if egress traffic to unexpected brokers/homeservers is flagged.
- Scrutinize VPN credential use — NightEagle's reliance on compromised VPN accounts routed through consumer tunnel services (Cloudflare WARP) is a pattern worth hunting for in authentication logs.
- Don't assume hacktivist tooling stays non-destructive — as documented with Hacking Cat, hacktivist-origin groups are increasingly adopting wiper and ransomware capability once associated mainly with organized crime and state actors.