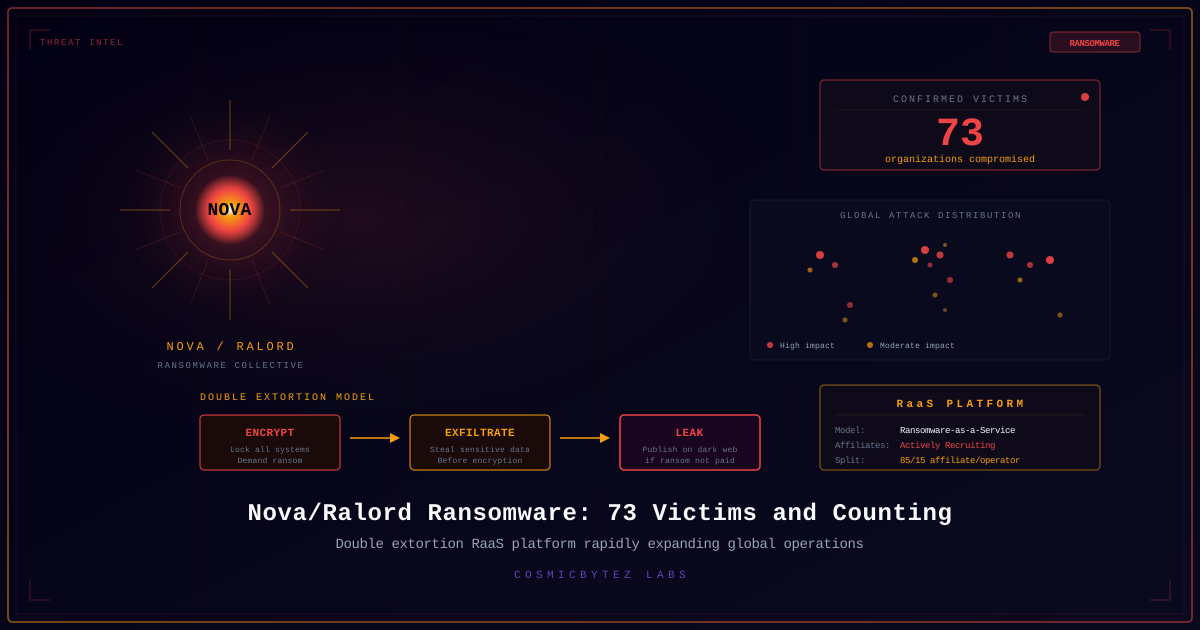
Rebranded and Fully Operational
The Nova ransomware group — formerly known as RALord — has been confirmed fully operational as of February 17, 2026, with 73 confirmed victims spread across nearly every continent. The group combines discipline with opportunism, targeting organizations across diverse sectors.
Group Profile
| Attribute | Details |
|---|---|
| Current Name | Nova |
| Former Name | RALord |
| Type | Ransomware-as-a-Service (RaaS) |
| Confirmed Victims | 73 |
| Reach | Global — nearly every continent |
| Tactics | Double extortion (encrypt + exfiltrate + leak) |
| Latest Activity | February 17, 2026 |
Double Extortion Model
Nova employs the now-standard double extortion approach:
- Encrypt — Lock down victim systems using ransomware payload
- Exfiltrate — Steal sensitive data before encryption
- Threaten — Demand payment or face public data leak
- Leak — Publish stolen data on dedicated leak site if ransom is not paid
Victim Distribution
Nova's targeting shows no particular geographic preference, hitting organizations across:
- North America — Largest concentration of victims
- Europe — Western European organizations prominently represented
- Asia — Growing number of victims in Southeast Asia
- South America — Brazil and Argentina targeted
- Africa — Emerging targeting in South Africa and Nigeria
- Oceania — Australian organizations affected
Evolving Ransomware Landscape
Nova is part of a broader trend where ransomware groups are pivoting tactics as victims increasingly refuse to pay:
| Trend | Description |
|---|---|
| DDoS-as-a-Service | Adding DDoS pressure on top of encryption and data theft |
| Insider recruitment | Recruiting employees at target organizations for initial access |
| Gig worker exploitation | Using freelance workers for money laundering and access brokering |
| Regulatory pressure | Reporting victims to regulators to increase pressure to pay |
| Customer notification | Directly contacting victim's customers about stolen data |
Defensive Recommendations
- Immutable backups — Maintain offline, air-gapped backups that cannot be encrypted
- Network segmentation — Limit lateral movement paths
- EDR/XDR deployment — Detect ransomware behavior before encryption begins
- Incident response plan — Have a tested plan specifically for ransomware scenarios
- Threat intelligence — Monitor Nova/RALord IOCs and TTPs
With 73 victims in just four months since rebranding, Nova demonstrates that ransomware remains one of the most prolific and profitable cybercrime models in 2026.
Sources
- Ransom-DB — Nova/RALord Ransomware Group Analysis 2026
- Bitdefender Threat Debrief — February 2026
- CYFIRMA — Weekly Intelligence Report February 2026