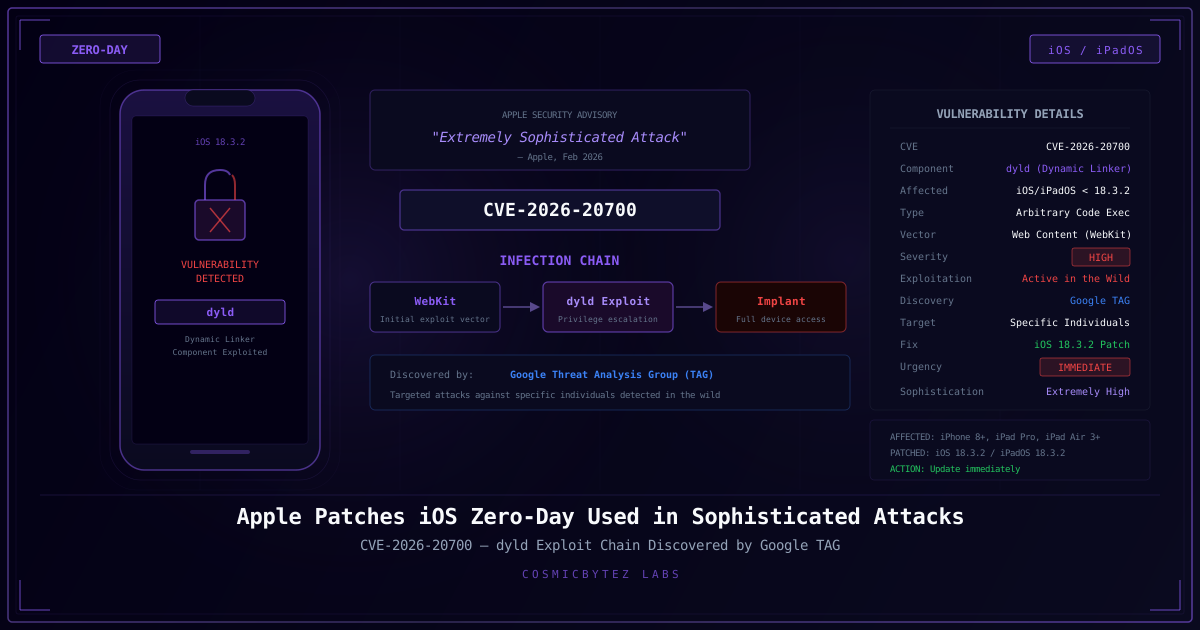
"Extremely Sophisticated" — Apple's Own Words
Apple has released emergency security updates across all platforms to patch CVE-2026-20700, a memory corruption vulnerability in dyld — Apple's dynamic linker. Apple described the attacks exploiting this vulnerability as "extremely sophisticated" — language the company rarely uses.
The vulnerability was discovered by Google's Threat Analysis Group (TAG), which specifically tracks nation-state actors and commercial spyware vendors.
Vulnerability Details
| Field | Details |
|---|---|
| CVE | CVE-2026-20700 |
| Component | dyld (dynamic linker) |
| Type | Memory Corruption |
| Severity | Critical |
| Exploitation | Confirmed in targeted attacks |
| Discovered By | Google Threat Analysis Group (TAG) |
| Target | Specific individuals |
Why dyld Is Critical
The dynamic linker (dyld) loads shared libraries when any application launches. It runs early in the startup chain with elevated privileges — a vulnerability here provides:
- Code execution before security checks initialize
- Universal exploitation — every app uses dyld
- Privilege escalation from user-level to system-level
The Full Infection Chain
CVE-2026-20700 was part of a multi-stage infection chain that includes two WebKit zero-days patched in December 2025:
Stage 1: Initial Compromise (WebKit Zero-Days)
├── CVE-2025-14174 — WebKit type confusion (RCE)
└── CVE-2025-43529 — WebKit sandbox escape

Stage 2: Persistence & Escalation (dyld Zero-Day)
└── CVE-2026-20700 — dyld memory corruption

Stage 3: Payload Deployment
└── Full device compromise with persistent implantThis chain is consistent with commercial spyware attack patterns — carefully constructed to achieve zero-click or one-click full device compromise.
Who Is Being Targeted?
Apple's "specific targeted individuals" language historically aligns with:
- Journalists investigating sensitive topics
- Human rights activists and dissidents
- Government officials and diplomats
- Opposition politicians in authoritarian states
Google TAG's involvement strongly suggests a commercial spyware vendor or nation-state intelligence agency.
Patched Versions
| Platform | Fixed Version |
|---|---|
| iOS | 26.3 |
| iPadOS | 26.3 |
| macOS Tahoe | 26.3 |
| watchOS | 26.3 |
| tvOS | 26.3 |
| visionOS | 26.3 |
How to Update
- iPhone/iPad: Settings > General > Software Update — Install iOS/iPadOS 26.3
- Mac: System Settings > General > Software Update — macOS Tahoe 26.3
- Apple Watch: Watch app > General > Software Update
- Apple TV: Settings > System > Software Updates
Defensive Recommendations
- Update all Apple devices immediately
- Enable Lockdown Mode for high-risk individuals (journalists, activists, executives)
- Enable Rapid Security Response for automatic critical patches
- Monitor for compromise indicators using tools like iVerify
Sources
- SecurityWeek — Apple Patches iOS Zero-Day Exploited in Extremely Sophisticated Attack
- Malwarebytes — Apple Patches Zero-Day in Targeted Spyware Attacks
- Help Net Security — Apple Zero-Day Fixed CVE-2026-20700