Executive Summary
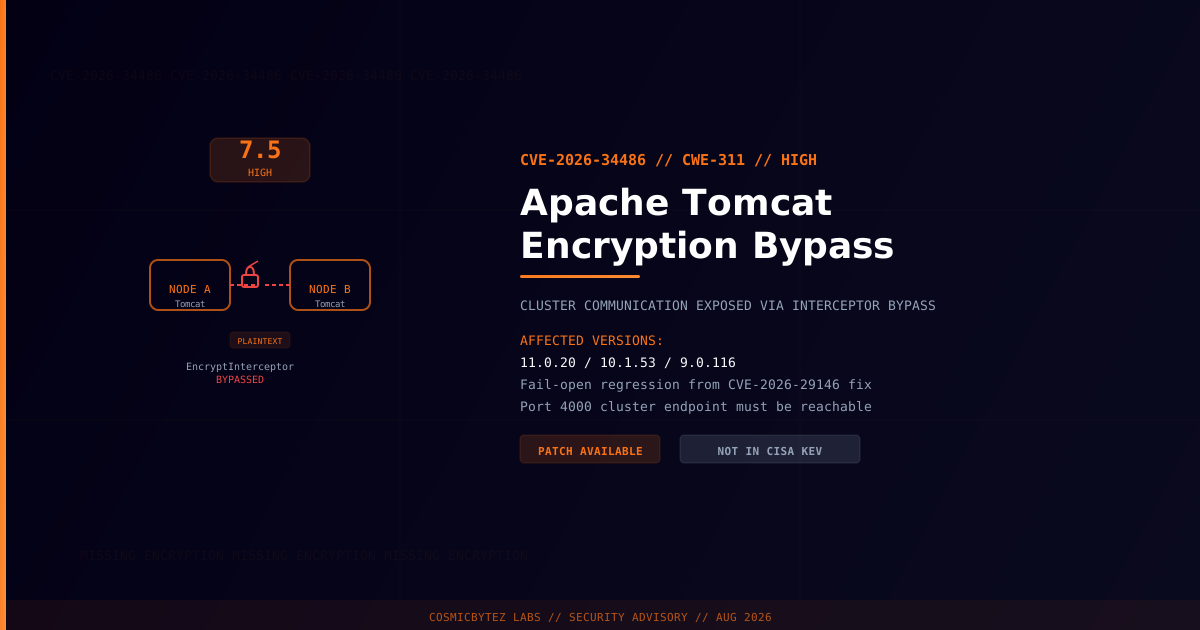
A high-severity vulnerability (CVE-2026-34486) has been disclosed in Apache Tomcat, allowing attackers to bypass the EncryptInterceptor component responsible for encrypting sensitive cluster communication data. The flaw stems from an incomplete fix for CVE-2026-29146 that introduced a fail-open regression — meaning the interceptor silently skips encryption under certain conditions rather than failing closed.
CVSS Score: 7.5 (High)
The vulnerability allows network-positioned attackers to intercept plaintext cluster communications between Tomcat nodes, potentially exposing credentials, session tokens, and other sensitive data transmitted between clustered instances. Patched versions were released on April 4, 2026.
Vulnerability Overview
| Attribute | Value |
|---|---|
| CVE ID | CVE-2026-34486 |
| CVSS Score | 7.5 (High) |
| CWE | CWE-311 — Missing Encryption of Sensitive Data |
| Type | EncryptInterceptor Bypass (Fail-Open Regression) |
| Attack Vector | Network |
| Authentication Required | No (network access to cluster port) |
| Discoverer | Bartlomiej Dmitruk, striga.ai |
| Reported | March 26, 2026 |
| Patched | April 4, 2026 |
Affected Versions
| Branch | Affected Version | Fixed Version |
|---|---|---|
| Tomcat 11.x | 11.0.20 | 11.0.21 |
| Tomcat 10.x | 10.1.53 | 10.1.54 |
| Tomcat 9.x | 9.0.116 | 9.0.117 |
Technical Details
Apache Tomcat's EncryptInterceptor is designed to encrypt all data transmitted between nodes in a Tomcat cluster, protecting sensitive information such as session data and cluster management traffic. CVE-2026-34486 arose as a fail-open regression introduced when patching the earlier CVE-2026-29146 Padding Oracle vulnerability.
Attack Scenario
1. Attacker positions themselves on the network path between Tomcat cluster nodes
2. Cluster nodes communicate over the default port 4000 (cluster replication endpoint)
3. Regression causes EncryptInterceptor to silently skip encryption under specific conditions
4. Attacker intercepts cluster communication in plaintext
5. Session data, credentials, and internal cluster management traffic exposed
6. Captured credentials or session tokens can be replayed for unauthorized accessExploitation Conditions
This vulnerability is conditionally exploitable — all three of the following must be true:
| Condition | Required? |
|---|---|
| Tomcat clustering feature enabled | Yes |
| Port 4000 reachable from attacker position | Yes |
| Affected version (11.0.20, 10.1.53, or 9.0.116) | Yes |
While the conditions narrow the attack surface, clustered Tomcat deployments are common in enterprise environments and the cluster replication port may be accessible within internal network segments or following an initial breach.
Remediation
Step 1: Upgrade to a Patched Version
# Download and deploy the patched version
# Apache Tomcat 11.0.21
wget https://dlcdn.apache.org/tomcat/tomcat-11/v11.0.21/bin/apache-tomcat-11.0.21.tar.gz

# Apache Tomcat 10.1.54
wget https://dlcdn.apache.org/tomcat/tomcat-10/v10.1.54/bin/apache-tomcat-10.1.54.tar.gz

# Apache Tomcat 9.0.117
wget https://dlcdn.apache.org/tomcat/tomcat-9/v9.0.117/bin/apache-tomcat-9.0.117.tar.gzStep 2: Verify Encryption Is Functioning
After upgrading, confirm that the EncryptInterceptor is active and encrypting cluster traffic:
<!-- In your server.xml cluster configuration -->
<Cluster className="org.apache.catalina.ha.tcp.SimpleTcpCluster">
  <Channel className="org.apache.catalina.tribes.group.GroupChannel">
    <Interceptor className="org.apache.catalina.tribes.group.interceptors.EncryptInterceptor"
                 encryptionAlgorithm="AES/CBC/PKCS5Padding"
                 encryptionKeyLength="128"/>
  </Channel>
</Cluster>Step 3: Restrict Cluster Port Access
# Restrict cluster replication port (default 4000) to known Tomcat nodes only
# Using iptables:
iptables -A INPUT -p tcp --dport 4000 ! -s <node-ip-range> -j DROP

# Or configure Tomcat's channel to bind to a specific interface
# In server.xml:
# <Receiver className="..." address="<internal-ip>" port="4000"/>Step 4: Disable Clustering If Not Required
<!-- Comment out or remove the Cluster element if not in use -->
<!-- <Cluster className="org.apache.catalina.ha.tcp.SimpleTcpCluster"> -->Detection
| Indicator | Description |
|---|---|
| Unexpected connections to port 4000 | Potential cluster replication traffic interception |
| Network captures showing plaintext cluster frames | Confirmation of EncryptInterceptor bypass |
| Session hijacking attempts post-cluster exposure | Sign of captured session token replay |
Verify Your Tomcat Version
# Check Tomcat version
catalina.sh version | grep "Server version"

# Or check the version file directly
cat /path/to/tomcat/lib/catalina.jar | unzip -p - org/apache/catalina/util/ServerInfo.propertiesPost-Remediation Steps
- Upgrade to Tomcat 11.0.21, 10.1.54, or 9.0.117
- Validate EncryptInterceptor configuration in
server.xml - Restrict port 4000 access via firewall to cluster node IPs only
- Monitor cluster port for anomalous connections
- Rotate any credentials or session data that may have transited the cluster during the vulnerable period
- Disable clustering if it is not actively used
References
- Red Hat Bugzilla — CVE-2026-34486
- Acunetix Vulnerability Database — CVE-2026-34486
- SentinelOne Vulnerability Database — CVE-2026-34486
- OpenCVE — CVE-2026-34486
- AWS ALAS — CVE-2026-34486