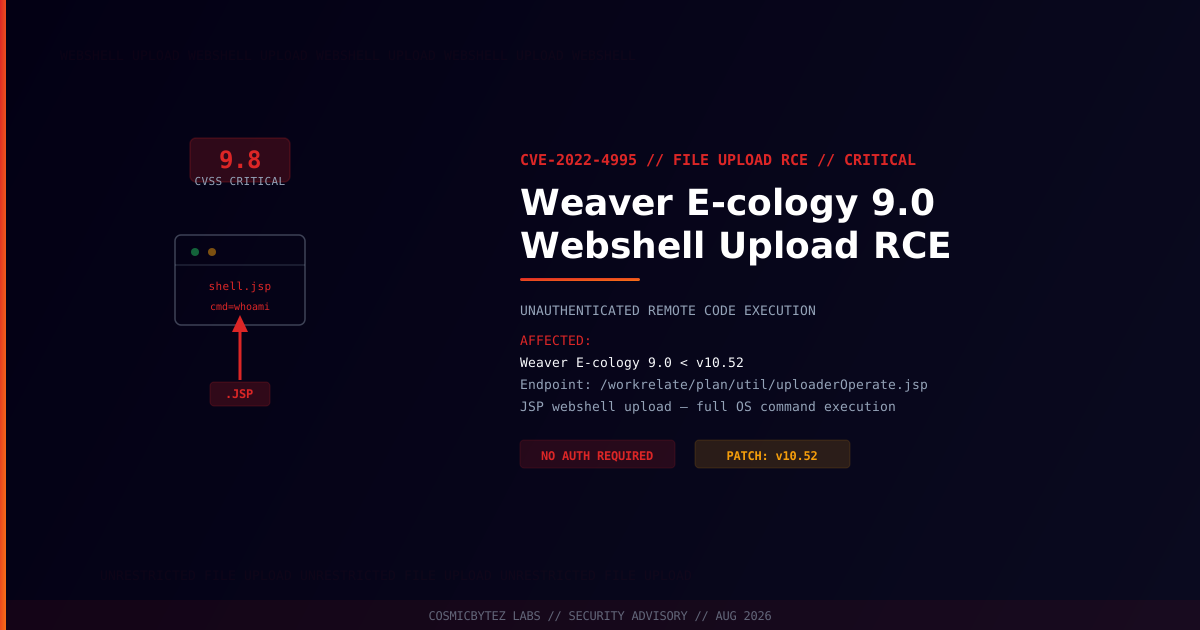
Executive Summary
A critical unauthenticated arbitrary file upload vulnerability (CVE-2022-4995) has been formally published for Weaver E-cology 9.0, a widely deployed enterprise collaboration and OA (Office Automation) platform popular across Asia-Pacific organizations. The flaw carries a CVSS 4.0 score of 9.3 and CVSS 3.1 score of 9.8, allowing unauthenticated remote attackers to upload JSP webshells through a vulnerable endpoint and achieve full remote code execution.
The Shadowserver Foundation first observed active exploitation of this vulnerability in October 2023, and active in-the-wild abuse is ongoing. Organizations running Weaver E-cology 9.0 below version 10.52 should patch immediately.
Vulnerability Overview
| Attribute | Value |
|---|---|
| CVE ID | CVE-2022-4995 |
| CVSS 4.0 Score | 9.3 (Critical) |
| CVSS 3.1 Score | 9.8 (Critical) |
| Type | Unrestricted File Upload (CWE-434) |
| Attack Vector | Network |
| Authentication Required | None |
| User Interaction | None |
| Published | August 7, 2026 |
| First Exploitation Observed | October 14, 2023 (Shadowserver) |
Affected Versions
| Software | Affected Versions | Fixed Version |
|---|---|---|
| Weaver E-cology | 9.0, versions before 10.52 | v10.52 |
Vulnerable Endpoint
The vulnerability exists in the file upload handler at:
/workrelate/plan/util/uploaderOperate.jsp
By manipulating the secId and plandetailid POST parameters, an unauthenticated attacker can bypass file type validation and upload arbitrary files — including JSP webshells — to a web-accessible directory.
Attack Chain
1. Attacker identifies Weaver E-cology 9.0 instance (commonly port 80/443)
2. Sends crafted POST request to /workrelate/plan/util/uploaderOperate.jsp
3. Manipulates secId + plandetailid parameters to bypass auth check
4. Uploads JSP webshell (e.g., shell.jsp) to web-accessible path
5. Accesses uploaded webshell via HTTP GET
6. Executes arbitrary OS commands as the application server process
7. Pivots to internal network, exfiltrates data, establishes persistenceSample Exploit Characteristics
POST /workrelate/plan/util/uploaderOperate.jsp HTTP/1.1
Host: target.example.com
Content-Type: multipart/form-data; boundary=----Boundary

------Boundary
Content-Disposition: form-data; name="secId"

<manipulated_value>
------Boundary
Content-Disposition: form-data; name="file"; filename="shell.jsp"
Content-Type: application/octet-stream

<%@ page import="java.io.*,java.util.*" %>
<% /* webshell content */ %>
------Boundary--Impact Assessment
| Impact | Description |
|---|---|
| Remote Code Execution | Execute arbitrary OS commands via webshell |
| Data Exfiltration | Access all E-cology data — HR, finance, workflows |
| Persistence | Webshell survives application restarts |
| Lateral Movement | Pivot to internal network from DMZ |
| Credential Harvesting | Access stored credentials and SSO tokens |
| Ransomware Staging | Common post-exploitation path in documented attacks |
Immediate Remediation
Step 1: Apply the Patch
Upgrade Weaver E-cology 9.0 to version 10.52 or later via the Weaver official security download portal. Contact Weaver's support team for enterprise upgrade assistance.
Step 2: Check for Existing Webshells
# Search for recently created JSP files in the web root
find /path/to/ecology/webroot -name "*.jsp" -newer /path/to/ecology/webroot/index.jsp -type f

# Check for common webshell patterns
grep -rl "Runtime.getRuntime().exec\|ProcessBuilder\|ScriptEngine" /path/to/ecology/webroot/

# Look for suspicious files in upload directories
find /path/to/ecology/webroot/upload -name "*.jsp" -o -name "*.jspx"Step 3: Immediately Block the Vulnerable Endpoint
If patching cannot be done immediately, block the vulnerable endpoint at the WAF or network perimeter:
# Nginx — deny access to the vulnerable endpoint
location /workrelate/plan/util/uploaderOperate.jsp {
    deny all;
    return 403;
}# WAF rule — block POST to vulnerable endpoint
Action: DENY
Request URI: /workrelate/plan/util/uploaderOperate.jsp
Method: POST
Step 4: Network Segmentation
- Restrict Weaver E-cology access to internal networks only where possible
- Ensure the application server cannot make outbound internet connections
- Deploy application-layer inspection for all E-cology traffic
Detection Indicators
| Indicator | Description |
|---|---|
POST to /workrelate/plan/util/uploaderOperate.jsp | Exploitation attempt |
New .jsp or .jspx files in upload paths | Successful webshell upload |
HTTP access to newly created .jsp files | Webshell execution |
| Outbound connections from application server | C2 communication or data exfiltration |
| Unusual process spawning from Java process | Command execution via webshell |
Threat Context
CVE-2022-4995 follows a pattern of critical vulnerabilities in enterprise OA platforms. Weaver E-cology has been targeted by multiple threat actors — including APT groups operating in the Asia-Pacific region — due to its widespread deployment in government agencies, financial institutions, and large enterprises.
The October 2023 first exploitation date (recorded by Shadowserver) predates the formal August 2026 CVE publication by nearly three years, indicating that the vulnerability has been actively exploited in the wild for an extended period while remaining untracked in public vulnerability databases.
References
- NIST NVD — CVE-2022-4995
- Shadowserver Foundation — First Exploitation Observed October 2023
- VulnCheck Advisory
- Weaver Security Downloads